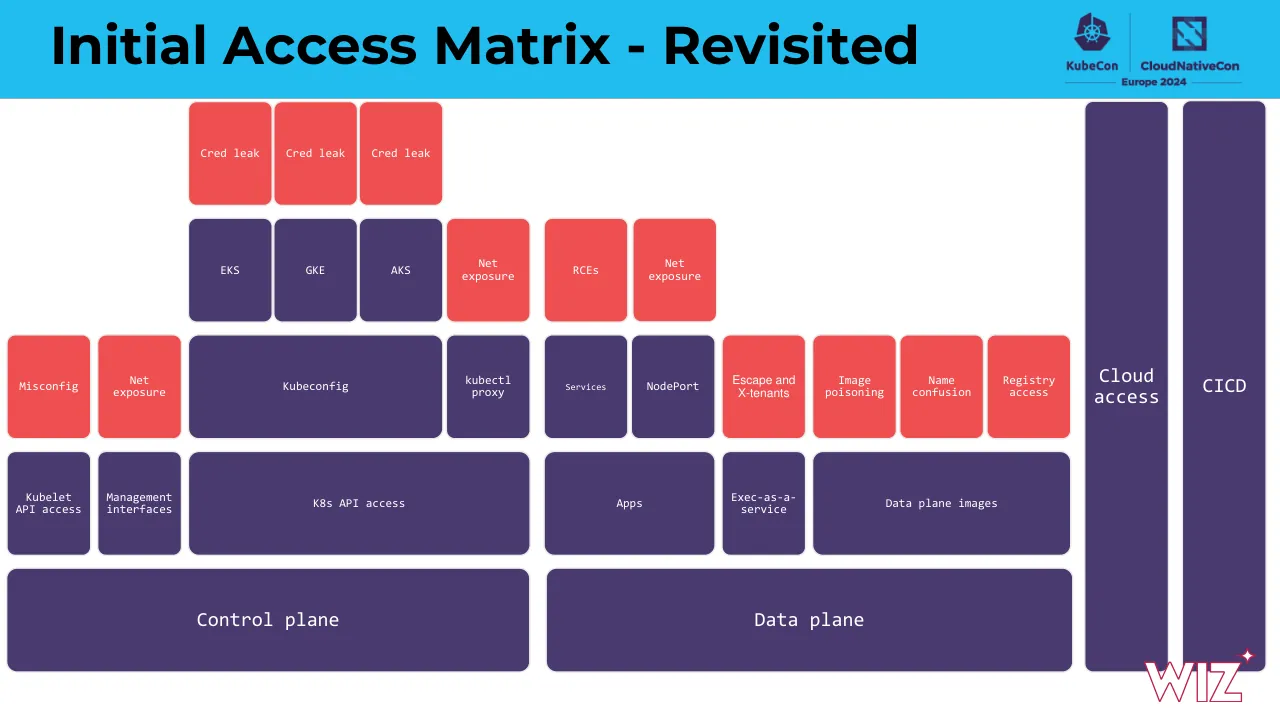
The deck opens with a KubeCon CloudNativeCon Europe 2024 title slide and an introduction to Shay Berkovich, Threat Research at Wiz, along with a short profile of his previous work. It then argues for studying initial access using a playful house metaphor, timing data on how quickly new clusters draw malicious scans, and a summary of attack-chain findings. The core sections begin with an architecture diagram and a methodology slide, followed by a toolbox of detection and protection layers. The attack surface is then covered in order. The control plane section addresses API server access, kubeconfig leaks, the kubelet API, management interfaces, kubectl proxy, and a system:authenticated misconfiguration case. The data plane section covers application RCEs, execution-as-a-service, NodePort, malicious images, and Leaky Vessels. A final section covers other angles. Each attack vector recurs with a matrix of detections and secondary controls so the audience can map vectors to defenses. The deck closes with a revisited initial access matrix, a Questions slide, and links to Wiz blogs, the NamespaceHound tool, the 2023 Kubernetes Security Report, and related research.
Slides worth studying
Questions about this deck
How many slides does the Wiz KubeCon Europe 2024 initial access deck have?
The deck has 62 pages in total. Slide 1 is the KubeCon CloudNativeCon Europe 2024 title slide.
How is the Wiz Kubernetes initial access deck structured?
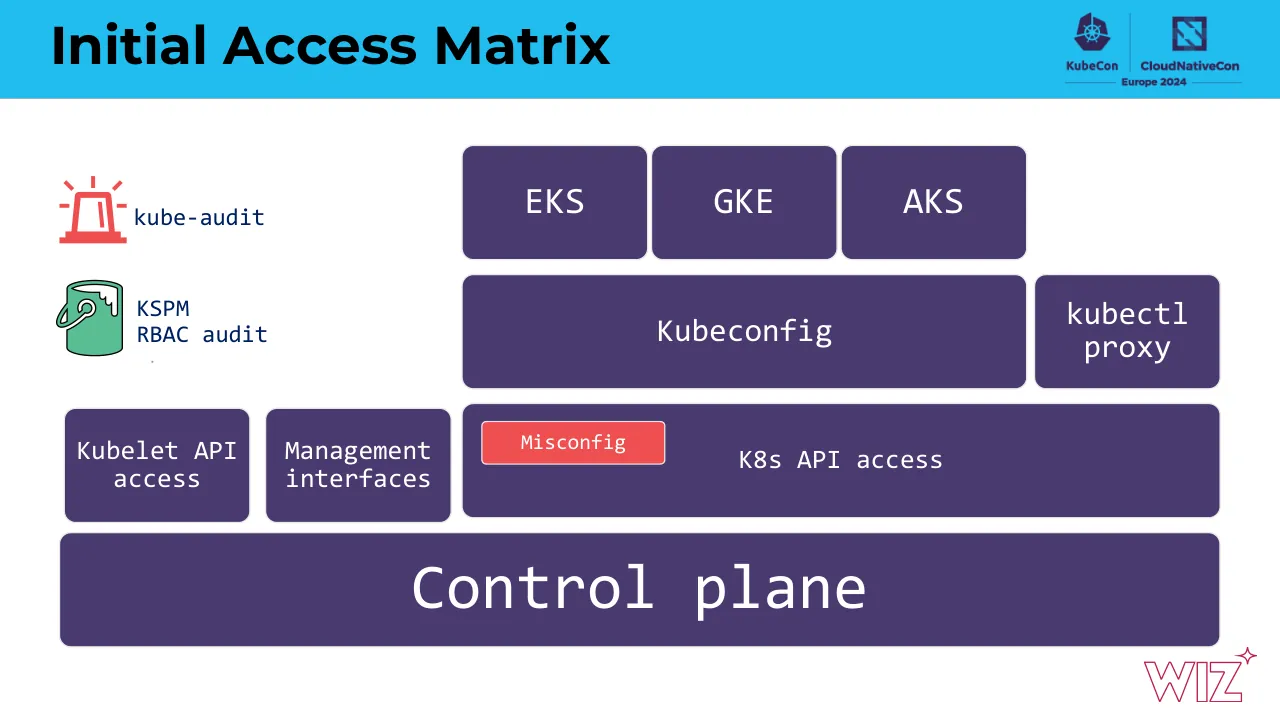
After the introduction and methodology, the deck covers the control plane starting at slide 10 and the data plane starting at slide 39. Slide 37 presents the Initial Access Matrix, and slide 38 follows with the matrix's kube-audit and RBAC audit detections.
What does the Wiz deck say about how quickly new clusters get malicious scans?
Slide 5 shows timing data from the 2023 Kubernetes Security Report: an EKS cluster received malicious scans in 22m, an AKS cluster in 2h 13m, and a GKE cluster in 2h 43m. The chart asks how long it takes a newly created cluster to get malicious scans.
What does the Wiz deck say about NodePort in Kubernetes clusters?
Slide 46 explains that a NodePort service has the control plane allocate a port from a range set by the --service-node-port-range flag, with a default of 30000-32767. Slide 47 estimates that ~6% of clusters have NodePort configured.
Details
- Company: Wiz
- Year: 2024
- Type: Conference talk
- Industry: Cybersecurity
- Pages: 62
Review score: 6 out of 10, Needs substantial work
Presentation quality, judged with the SlideDeck Co review heuristic. Ask, evidence and idea merit are not rated here.
The route is clear and disciplined: a metaphor and framing (slides 4-6), an architecture map (7), then each vector recurs with the same alarm and bucket icons for detections and controls, and a layered matrix builds up (33, 37, 52, 61) and pays off on the revisited matrix (61). But many pages are weak as standalone slides: slide 55 is nearly blank, slide 36 has a tiny diagram with a stray icon, slides 26 and 38 are dense terminal dumps, and slide 14 has overlapping screenshots. The final matrix (61) has tiny unreadable labels, and the Home Alone stills on slides 27, 30, 34 and 53 and the repeated door thumbnails carry mood but little information. The core argument is recoverable for a live talk, but the pages need substantial revision to work without the speaker.
Worth keeping: Keep the repeated vector structure with the alarm and bucket icons, and the stacked purple and red matrix on slide 37 that builds toward the final map.
Most useful repair: Enlarge or crop the code, terminal and log screenshots (slides 15, 18, 26, 38) to the few lines that matter, and enlarge the labels on slide 61 so the closing matrix can be read.
What would change the score: Remove or replace the empty and decorative pages (55, 36 icon, 47, 49), fix the overlapping images on slides 13 and 14, and correct the 'Managment' typo and the French 'Boîte à outils' heading on slide 9.
Confidence medium. 62 of 62 pages inspected on contact sheets, 4 at readable size. Reviewed 2026-11-08. Model-assisted review (claude-sonnet-5-5).
Full text of the slides (62 slides)
Every slide's words and a description of its charts and images, so the deck can be searched and rebuilt. Also available as Markdown.
Slide 1
KubeCon / CloudNativeCon / Europe 2024
Visuals: Illustration: a flat paper-cut style Paris skyline along the bottom right, spanning roughly x 40% to 100%, y 46% to 100%. Landmarks from left to right: a green domed building (Panthéon-like) at about x 42-53%, a salmon-pink triumphal arch at about x 54-61%, a blue Sacré-Cœur-like basilica at about x 63-71%, a large red Eiffel Tower at about x 71-79%, a peach Louvre pyramid building at about x 76-91%, and red Notre-Dame towers at about x 90-98%. A red arch-frame (La Grande Arche style) stands at about x 55-67%, y 69-100%. The skyline sits on a light grey cloud-fringed base at the bottom. Dark purple silhouette buildings sit behind. Four paper-style clouds in white-to-light-blue gradient with soft grey-blue shadows: one large at top right (x 72-91%, y 6-27%), one medium at right (x 87-96%, y 47-58%), one small at x 41-50%, y 58-68%. A large light-blue (#5BD3F5) circular arc fills the upper right; a darker teal-blue (#41A3CB) curved band runs in the lower left from x 0-40%, y 63-100%. Flat vector style, no photographs.
Slide 2
Why Barricade the Door if the
Window Is Open?
Making Sense of Kubernetes Initial Access Vectors
Shay Berkovich – Threat Research @ Wiz
Visuals: Abstract geometric illustration filling the whole slide. A saturated blue #22BDEF area occupies the upper-left and the bottom edge. A light grey #E9E8E6 area occupies the upper-right and right, separated from the blue by a straight diagonal edge that runs from about x 68.7%, y 0% down to about x 12.5%, y 100%. A large blue circular arc with its edge running from about x 100%, y 39% to x 56.5%, y 100% sits in the lower-right, with its interior in grey on the upper-right side. A lighter cyan-blue #5BD6F5 rectangle sits inside the arc at about x 75.6% to 100%, y 53.5% to 86.6%, with a hard square corner at its left and bottom edges. There are no photographs, charts, logos, or icons. The shapes are flat with no gradients, shadows, or outlines.
Slide 3
@quisuisje
Previous life – SW dev
Usenix and EuroSys AEC member
BlueCoat -> Symantec -> BlackBerry -> Wiz
Previous research in
Published papers and journal articles in Runtime Verification (??what??)
UBCIS – benchmark for container image scanning
NamespaceHound
Falco bypasses
Cluster Grey Zone
2023 Kubernetes Security Report
Everything Kubernetes security
Visuals: Two logos at top right: the KubeCon logo (purple Kubernetes wheel mark above the word KubeCon in dark bold text) and the CloudNativeCon logo (purple square mark with a stylised N-like design above the words CloudNativeCon, with the line 'Europe 2024' beneath both, separated by a thin vertical divider and short horizontal rules). Bullet glyphs are small black Kubernetes ship-wheel icons, one per main item. A small grey dot sits below the third bullet line. Bottom right: the Wiz logo in outlined red/crimson stroke lettering 'WIZ' with a four-point sparkle at its top right corner. No photographs or charts.
Slide 4
Cluster-as-a-House / KubeCon / CloudNativeCon / Europe 2024 / * from r/Sims4 channel
Visuals: Photograph: a snowy Sims 4 rendering of a two-storey red-brick Colonial-style house, seen from the front three-quarter angle. Two dormer windows sit in the snowy roof, and a white pillared entrance porch with a pediment is at the centre. A small wreath hangs on the front door. Two tall pine trees with snow-laden branches frame the house on the left and right. Foreground elements are a snow-covered hedge, a low brick wall with stone caps, a red-and-white fire hydrant, white bollards, a wrought-iron fence along the kerb, and a dark manhole cover. Falling snowflakes and soft white bokeh particles fill the frame. Lighting is soft and diffuse, like overcast winter daylight. Dominant colours are white snow, red brick, dark green pine and grey-white sky. The image is a full rectangle with no crop, shown as a boxed photo with no border, overlay or tint. Logos: KubeCon and CloudNativeCon Europe 2024 logo lockup at top right, with the KubeCon ship-wheel mark in dark purple and the CloudNativeCon square-N mark in dark purple beside it. Wiz logo at bottom right, outlined in crimson.
Slide 5
Why Initial Access?
KubeCon / CloudNativeCon / Europe 2024
From Exposure to Discovery: How Long Does It Take for a Newly Created / Cluster to Get Malicious Scans?
EKS cluster
22m
AKS cluster
2h 13m
GKE cluster
2h 43m
WIZ Research
* From The 2023 Kubernetes Security Report
Visuals: One dark illustrated diagram of three horizontal timelines inside a boxed image (not cropped, not full-bleed). Chart title: From Exposure to Discovery: How Long Does It Take for a Newly Created Cluster to Get Malicious Scans? Three rows, each showing a cluster icon and a bomb-like graphic on the left, a white curved fuse line running right to a small purple starburst. Row 1: EKS cluster, label 22m, fuse ends at about 22 minutes. Row 2: AKS cluster, label 2h 13m, fuse ends at about 2 hours 13 minutes. Row 3: GKE cluster, label 2h 43m, fuse ends at about 2 hours 43 minutes. Each cluster icon is a blue (#0A5CE6) circle with a white Kubernetes helm wheel, overlapped by a pink (#FF8AE8) striped sphere with a dark fuse nub. Fuse lines are off-white (#E6E6E6), about 2 px wide. Starbursts are purple-to-blue gradient (#8A5CF6 to #5A7CF0). Labels are white sans-serif. Lighting is flat; no photograph. Dominant colours: charcoal #26262F background, blue, pink, white. Bottom-right of the image holds a white WIZ Research wordmark. Logos: KubeCon mark with wordmark, CloudNativeCon mark with wordmark, WIZ outline logo at bottom right of slide.
Slide 6
Why Initial Access?
Whiz logo area: KubeCon / CloudNativeCon / Europe 2024
K8 attack chain study results: once an attacker is in the cluster, there is not much in place to stop them
Attacker
Initial Access
Control plane
Anonymous API access
kubectl proxy
Sensitive interfaces
Data plane
Image poisoning
App vulnerability
Management interfaces
Lateral Movement
Namespace separation
Network policies
Privilege Escalation
Container escape
RBAC permissions
Impact
Cluster
DoS of K8s services
Local secrets
Cryptomining
Cloud
Cloud secrets
Image poisoning
Other clusters
Cloud cryptomining
WIZ Research
https://www.wiz.io/blog/key-takeaways-from-the-wiz-2023-kubernetes-security-report
Visuals: Diagram (flowchart) on a near-black navy background with a title line at top centre reading 'K8 attack chain study results: once an attacker is in the cluster, there is not much in place to stop them' in white sans-serif. On the left, a purple-outlined hooded figure holding a laptop, labelled 'Attacker', with a magenta arrow pointing right into a rounded purple-outlined box labelled 'Initial Access' containing two inner blue-outlined boxes: 'Control plane' (Anonymous API access, kubectl proxy, Sensitive interfaces) and 'Data plane' (Image poisoning, App vulnerability, Management interfaces). Blue arrows from the Initial Access box run up-right to a purple-outlined box 'Lateral Movement' (Namespace separation, Network policies) and down-right to a purple-outlined box 'Privilege Escalation' (Container escape, RBAC permissions). These two boxes sit inside a large dashed-outline rounded rectangle with a slightly purple-tinted fill. Two vertical arrows between them: a magenta-to-purple arrow pointing down and a blue arrow pointing up. From Lateral Movement a blue arrow goes right to a purple-outlined box 'Impact'; from Privilege Escalation a blue arrow goes right to the same Impact box. Impact contains two blue-outlined boxes: 'Cluster' (DoS of K8s services, Local secrets, Cryptomining) and 'Cloud' (Cloud secrets, Image poisoning, Other clusters, Cloud cryptomining). Bottom right of the diagram, the white stylised text logo 'WIZ' followed by 'Research' in white. The diagram is a boxed raster image, not cropped, with no overlay; dominant colours are near-black #25252F background, purple-magenta #C05BE0 outlines, blue #1F5BFF connectors and outlines. Header logos: KubeCon (purple Kubernetes wheel mark, #3D2C6B) and CloudNativeCon (purple-and-white square mark, #3D2C6B) with the text 'Europe 2024' in dark navy. Bottom-right Wiz logo: outlined red-magenta wordmark 'WIZ' with a four-point sparkle, colour #C8102E.
Slide 7
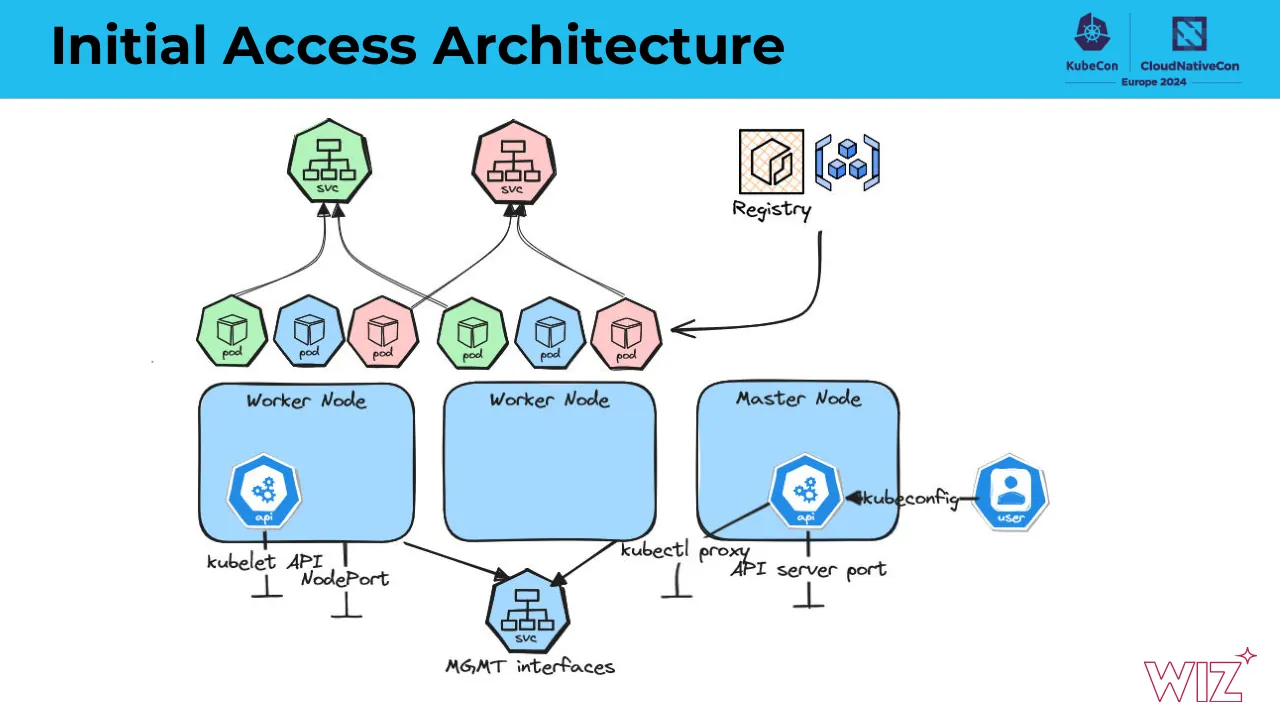
Initial Access Architecture / Registry / Worker Node / Worker Node / Master Node / api / user / kubeconfig / kubelet API / NodePort / kubectl proxy / API server port / MGMT interfaces / svc / svc / svc / pod / pod / pod / pod / pod / pod
Visuals: Hand-drawn style architecture diagram, full colour, with black sketch-style outlines and arrows. Top row: two heptagon-shaped service icons, the left one green (#8BE08B) and the right one pink (#FFC4C4), each containing a small tree-of-boxes icon and the label 'svc' in black. Middle row: six heptagon pod icons with cube symbols and the label 'pod' beneath each, in colour order green, blue (#A3D4FF), pink, green, blue, pink. Thin black arrows run from the pods upward to the two svc icons: the first two pods point to the left svc, and the pod third from the left and the fourth pod point to the right svc. A registry icon at upper right consists of an orange hatched square box with a cube-in-box symbol and a cluster-of-blue-cubes icon beside it, labelled 'Registry' in handwriting; a large black curved arrow runs from below the Registry label down and left to the right-most pod. Lower row: two rounded light-blue rectangles labelled 'Worker Node' (left and middle) and one labelled 'Master Node' (right), each with black outlines. Inside the left worker node is a blue heptagon Kubernetes API icon labelled 'api'; the master node contains a similar 'api' icon. A blue user icon labelled 'user' sits to the right of the master node, connected by a black arrow labelled 'kubeconfig' pointing into the master api icon. Short black tick-ended lines hang below the nodes and labels 'kubelet API', 'NodePort', 'kubectl proxy' and 'API server port' mark them. A light-blue svc heptagon labelled 'MGMT interfaces' sits at bottom centre, with an arrow from the left worker node and an arrow from the middle worker node pointing to it. Colours: light blue #A3D4FF, cyan band #22BDEE, green #8BE08B, pink #FFC4C4, dark blue api icons #1E7FE0, orange hatch #F5B27A.
Slide 8
Methodology
KubeCon | CloudNativeCon
Europe 2024
How attackers get in?
Detections tripped
Security controls
Visuals: Three photographs in a left-to-right sequence joined by two right-pointing arrows. (1) Photo of a red front door with a brass knocker and brass letterbox, set in white door surround with sidelights and windows, framed as a portrait rectangle, not cropped, bright daylight, dominant colours red, white and green foliage. (2) Photo of a basement-like interior rendered as a dim grey and brown scene with a wooden staircase banister, a dotted grey wall and red laser-style beams crossing the space, landscape rectangle, not cropped. (3) Still of a man in a dark patterned fur-trimmed coat and black hat in a room with patterned wallpaper, another figure blurred at left, landscape rectangle, not cropped, warm indoor lighting, faint illegible watermark at bottom right. Two block arrows: light blue #4DB3E6 fill with dark navy #1F4E79 outline, pointing right, between photo 1 and 2 and between photo 2 and 3. A red siren icon (#EF4D4D) with flashing light rays below the Detections tripped caption. A green paint roller/bucket icon (#59BF92) with white drip marks and a black outline below the Security controls caption. Wiz logo in crimson outline (#C8193C) at bottom right.
Slide 9
Boîte à outils
System-level
detections/protections
K8s Admission
Controller
kube-audit log-based
detections
Cloud logs and
detection solutions
KubeCon
CloudNativeCon
Europe 2024
Cloud
Cloud
detections
Cloud
logs
Kubernetes
K8s AC
K8s
audit log
Container
Container
Container
K8s-
aware
sensor
VPC flow
logs
VM / Kernel
Hardware
WIZ
Visuals: Hand-drawn style architecture diagram on white. Outer large dashed black rounded rectangle labelled 'Cloud' (top) spanning most of the width on the right half. Inside it, a second dashed rounded rectangle labelled 'Kubernetes'. Inside Cloud at top: green hatched ellipse 'Cloud detections' at upper left, and green hatched ellipse 'Cloud logs' at upper right. Inside Kubernetes: green hatched ellipse 'K8s AC' at upper left, green hatched ellipse 'K8s audit log' at upper right. Three black rounded rectangles labelled 'Container' in a row inside Kubernetes. A green hatched ellipse 'K8s-aware sensor' overlaps the third Container box and the VM / Kernel bar. A black rounded rectangle 'VM / Kernel' spans the width below the containers. Green hatched ellipse 'VPC flow logs' at lower right inside Cloud. Black rounded rectangle 'Hardware' at the bottom below the Cloud boundary. Green hatching on ellipses, black sketchy outlines. Logos: KubeCon (dark navy Kubernetes wheel icon with wordmark), CloudNativeCon (dark navy stylised square icon with wordmark), Wiz (red outlined wordmark with sparkle).
Slide 10
Control Plane
WIZ
Visuals: Background illustration, full-bleed: a flat geometric composition. A saturated sky-blue (#21BDF0) field occupies the upper-left, cut by a 45-degree diagonal edge from bottom-left (about x 12.5%, y 100%) to top-right (about x 68.7%, y 0%). The lower-right area is light warm grey (#E9E8E6). A large sky-blue circular arc (#21BDF0) rises from the bottom edge near x 56% and sweeps up to the right edge at about y 39%, forming the edge of a large circle. Inside the arc, a lighter cyan rectangle (#5CD5F5) fills the right side from about x 75.6% to the right edge and from about y 53.7% to y 86.6%, with its left edge straight and its top edge meeting the arc. The graphic has no gradients, shadows or photographic content. The WIZ logo (see elements) is the only other visual.
Slide 11
K8s API Access / Public vs. private clusters / 69% / Public / Private / WIZ Research / KubeCon / CloudNativeCon / Europe 2024
Visuals: Photograph of a red front door: a brass door knocker and brass letterbox sit on a red six-panel door, flanked by white sidelights with black iron grilles and a white painted surround. A fanlight with greenery shows above. A black boot scraper is at the bottom right and the step is grey pavement. The photo is a rectangular boxed image, not cropped, with no border or overlay. Pie chart titled Public vs. private clusters. Two slices: Public, a large slice of about 69% in bright blue (#0055EE approximately), with the printed label 69% in white near its centre; Private, a smaller slice of about 31% (estimated, not printed) in pink (#FF80FF approximately), pulled out slightly from the pie. No axes. Legend at the bottom centre: blue square with Public, pink square with Private. Wiz Research wordmark at bottom right of the panel in white. Chart panel background is dark charcoal (#25252F approximately). Outlined Wiz logo at bottom right of slide in crimson-pink outline.
Slide 12
K8s API Access
Default access
Anonymous auth enabled
(EKS,GKE)
Cluster version / flavor
Health OK
Certificate details
K8s RBAC can interfere!
KubeCon
CloudNativeCon
Europe 2024
WIZ
Visuals: Three overlapping browser-window screenshots (Chrome-style, light grey toolbars, red 'Not secure' pills with red x-circle icons, struck-through 'https' in the address bar). Back window (top-right, at about 49.6% x, 16% y, 44.4% w, 30.7% h, bordered in light blue #5BB8E8): address bar 'https://34.31.162.55/api' with partially visible JSON beginning '{ "kind": ... "apiVer..." "metadata" "status" "message" "reason" "details" "code": }' in monospace dark text on white. Middle window (about 55.4% x, 22.2% y, 32.9% w, 31.5% h, light blue border): address bar 'https://34.31.162.55/version' with JSON showing "major": "1", "minor": "2...", "gitVersion", "gitCommit", "gitTreeState", "buildDate", "goVersion", "compiler": "gc", "platform": "linux/amd64" within braces. Front small window (about 63.1% x, 33.7% y, 31.8% w, 13.1% h, light blue border): address bar 'https://34.31.162.55/healthz' with body text 'ok'. Small door photograph (about 1.5% x, 83.5% y, 5.7% w, 14.0% h): a red front door with a brass knocker and fanlight-style white framed sidelights, white painted frame, shown full door, straight-on, daylight; dominant colours red, white, and dark green-grey foliage at top; boxed, not cropped. Wiz logo: outlined red-magenta wordmark with a sparkle at the top right, bottom-right corner, about 88% x, 91% y. KubeCon logo: dark purple Kubernetes wheel emblem above 'KubeCon'; CloudNativeCon logo: dark purple square emblem with white diagonal mark beside 'CloudNativeCon' and 'Europe 2024' beneath, separated by a thin vertical divider.
Slide 13
K8s API Access
What happens if…
system:anonymous != trivial
system:unauthenticated != trivial
Not secure
https://34.31.162.55/api/v1/namespaces/default/pods
{ "kind": "Status", "apiVersion": "v1", "metadata": {}, "status": "Failure", "message": "pods is forbidden: User \"system:anonymous\" ... ", "reason": "Forbidden", "details": { "kind": "pods" }, "code": 403 }
Not secure
https://34.31.162.55/api/v1/namespaces/default/p...
{ "kind": "PodList", "apiVersion": "v1", "metadata": { "resourceVersion": "145972318" }, "items": [ { "metadata": { "name": "andy-dufresne", "namespace": "default", "uid": "2fb4609f-2bc0-4f61-8289-a4428295ffb9", ...
alamy
13002
Visuals: Two screenshot images of browser windows showing JSON API responses. Screenshot 1 (x 5.2, y 46.9, w 76.9, h 34.0 measured, visible window roughly x 5.2 to 50, y 46.9 to 81) has a light grey toolbar with back, forward and reload arrows, a red 'Not secure' pill with a red X icon, and a struck-through red 'https' prefix before '://34.31.162.55/api/v1/namespaces/default/pods'; its body is a monospace JSON Status response with reason Forbidden and code 403 on white. Screenshot 2 (x 36.9, y 55.5, w 45.2, h 34.3) is a second browser window with the same toolbar and a PodList JSON response with resourceVersion 145972318 and an item named andy-dufresne, cropped at the bottom edge of the window. Both windows have thin light blue #5BAEE6 borders and sit on white. Photograph A (x 78.6, y 21.3, w 13.8, h 39.6): a tall portrait photo of a red front door open inward in a white-trimmed doorway beside a stone wall with the house number 13002 in black vertical digits, shown in colour with a dark strip and alamy watermark along the bottom; dominant colours red, cream and grey stone; daylight; boxed, not full-bleed. Photograph B (x 1.5, y 83.5, w 5.7, h 14.0): a small portrait photo of a closed red front door with a brass knocker and white trim and sidelights, bright daylight, boxed with no border. Logos: KubeCon logo (purple Kubernetes wheel mark above the word KubeCon, dark purple #4B2A6B) and CloudNativeCon logo (dark purple square mark above the word CloudNativeCon, dark purple #4B2A6B) separated by a thin vertical divider, with 'Europe 2024' beneath in dark purple between thin horizontal rules; Wiz logo in red-outlined wordmark #E0245E with a four-point sparkle at the top right. Bullet icon: a small dark navy Kubernetes helm wheel glyph before 'What happens if…'.
Slide 14
K8s API Access / Clusters with non-trivial anonymous access / <1% / Public Managed Clusters / Public Managed Clusters With Non-Trivial Anonymous Access / WIZ Research / WIZ Research / KubeCon / CloudNativeCon / Europe 2024
Visuals: One pie chart titled 'Clusters with non-trivial anonymous access', drawn on a dark charcoal panel. The chart has a single large blue slice (about 99%, unlabelled except by the legend) and a thin pink slice at about 12 o'clock labelled '<1%'. Legend, from top: blue square 'Public Managed Clusters'; pink square 'Public Managed Clusters With Non-Trivial Anonymous Access'. No axes, no highlighted points beyond the pink slice. Photograph: a white-painted residential front door frame with a small leaded sidelight window containing black ironwork and a glimpse of green foliage above, and a bright red panelled front door with a brass knocker, silver door knob and a brass letter plate; a black threshold and white stone steps at the bottom. The photograph is cropped on its right side by the chart panel, is boxed (not full-bleed), has no overlay, and is lit by even daylight with dominant colours white, red and black. Chart panel and upper panel are flat, with no shadow.
Slide 15
K8s API Access / kube-audit log / 2024-02-08T15:54:02.449+02:00 {"kind":"Event","apiVersion":"audit.k8s.io/v1","level":"Request / { / "kind": "Event" / "apiVe / "level / "audit / "stage / "reque / "verb / "user / "u / "g / ] / }, / { / insertId: "269c6dfe-dece-4de7-aeda-b91f7bfcebde" / labels: {2} / logName: "projects/attack-simulation-lab-371416/logs/cloudaudit.googleapis.com%2Fdata_access" / operation: {4} / protoPayload: { / @type: "type.googleapis.com/google.cloud.audit.AuditLog" / authenticationInfo: { / principalEmail: "system:anonymous" / } / authorizationInfo: [1] / methodName: "io.k8s.core.v1.pods.list" / requestMetadata: {2} / resourceName: "core/v1/namespaces/default/pods" / serviceName: "k8s.io"
Visuals: Red alarm/siren icon (outline style, red #EF4444-ish, about 5% wide, centred above the subtitle, rays above and around the beacon, with a flat base). Small black Kubernetes helm (ship wheel) bullet icon left of the subtitle. Two overlapping screenshot panels of a Google Cloud Logging JSON viewer: the back panel (light grey #F2F4F3 with thin blue #4A9FE0-ish border) shows a timestamp line 2024-02-08T15:54:02.449+02:00 and a partly hidden JSON object with keys kind, apiVersion, level, audit, stage, request, verb and user, cut off by the front panel; the front panel (white background, thin light blue border) shows an expanded JSON tree with insertId 269c6dfe-dece-4de7-aeda-b91f7bfcebde, labels {2}, logName projects/attack-simulation-lab-371416/logs/cloudaudit.googleapis.com%2Fdata_access, operation {4}, protoPayload expanded with @type type.googleapis.com/google.cloud.audit.AuditLog, authenticationInfo principalEmail system:anonymous, authorizationInfo [1], methodName io.k8s.core.v1.pods.list, requestMetadata {2}, resourceName core/v1/namespaces/default/pods, serviceName k8s.io. Keys are dark grey, string values are blue (#1A56C4-ish), triangles are dark grey disclosure arrows. Small door photograph bottom-left (about 6% wide, boxed, unrounded): a red front door with a brass knocker, white pilasters and fanlight/sidelights, framed by a white painted entrance, lit by daylight, dominant colours red and white. Wiz logo bottom-right in crimson outline lettering with a small sparkle. KubeCon and CloudNativeCon Europe 2024 logos top-right in dark purple and navy.
Slide 16
K8s API Access
Anomaly rules on kube-audit
Secondary detections
KSPM
RBAC audit
Network exposure management
Secondary protection – AC / cloud policies
WIZ
Visuals: Red alarm/siren icon (flat outline style, about 9% wide, centred over the left column, approx x 32-40%, y 17-27%) with rays above it. Green paint-can icon (flat, filled #59BF92 with black outline, x 67.3, y 17.5, w 5.4, h 10.4) with a drip and a curled handle. Photograph of a red front door with white painted frame, sidelights and brass knocker, shown full-frame in a small unboxed image at bottom left (x 1.5, y 83.5, w 5.7, h 14.0), sunlit, centred composition, dominant colours red and white. Logos top right: KubeCon logo (purple Kubernetes wheel mark with 'KubeCon' wordmark), vertical divider, CloudNativeCon logo (dark purple square mark with 'CloudNativeCon' wordmark), and 'Europe 2024' text with horizontal rules beneath. Bottom right: Wiz logo in outlined crimson (#C8103E-like) lettering with a four-point sparkle at top right. Bullet glyphs are small black Kubernetes ship-wheel icons before each bullet item.
Slide 17
kubeconfig
Do you know what you
have in
~/.kube/config?
apiVersion: v1
clusters:
- cluster:
certificate-authority-data:
LS0tL...
server: IP
name: cluster1
- cluster:
...
contexts:
- context:
cluster: cluster1
user: user1
name: context1
- context:
...
kind: Config
preferences: {}
users:
- name: user1
user:
- name: user2
user:
- name: user3
Visuals: A black rectangular code panel (#000000) at x 49.5%, y 17.9%, width 32.6%, height 76.7%, with a thin light blue (#5BC0EB-like) border, containing monospaced white (#FFFFFF) YAML text showing a kubeconfig file: apiVersion: v1; clusters: with a cluster entry containing certificate-authority-data: LS0tL... and server: IP, name: cluster1, an ellipsis line; contexts: with a context entry (cluster: cluster1, user: user1, name: context1) and an ellipsis line; kind: Config; preferences: {}; users: with entries name: user1 / user:, name: user2 / user:, name: user3. Three yellow (#FFC000) key icons stacked vertically at approximately x 30.5-36.0%, aligned with the user1, user2 and user3 lines, each with a white circular hole at the bow and a serrated blade pointing right toward the panel. A small KubeCon logo (dark purple Kubernetes wheel emblem with the word KubeCon beneath) and a CloudNativeCon logo (dark purple square icon with the words CloudNativeCon and Europe 2024 beneath, separated by a vertical divider) sit in the header at top right. A Wiz logo (red-magenta outlined wordmark with a sparkle) sits at the bottom right. A Kubernetes ship's wheel bullet icon in black precedes the question text. A tiny dot appears at approximately x 11.8%, y 50%.
Slide 18
kubeconfig - EKS
KubeCon
CloudNativeCon
Europe 2024
Do you know what you
have in
~/.kube/config?
Don’t run untrusted
kubeconfig’s
(equivalent to local
executions)
- name: arn:aws:eks:eu-central-
1:xxxxxxxxxxxx:cluster/demo-cluster
user:
exec:
apiVersion:
client.authentication.k8s.io/v1beta1
args:
- --region
- eu-central-1
- eks
- get-token
- --cluster-name
- wizard-maker-cluster
command: aws
env:
- name: AWS_PROFILE
value: demo1
- name: arn:aws:eks:eu-central-
1:xxxxxxxxxxxx:cluster/demo-cluster
user:
exec:
apiVersion:
client.authentication.k8s.io/v1beta1
args:
- token
- -i
- wiz-k8s-cluster
command: aws-iam-authenticator
env:
- name: AWS_STS_REGIONAL_ENDPOINTS
value: regional
- name: AWS_DEFAULT_REGION
value: eu-north-1
interactiveMode: IfAvailable
provideClusterInfo: false
WIZ
Visuals: Two black terminal panels with white monospace text showing kubeconfig YAML for an AWS EKS cluster. Panel 1 (back, top-left) runs from about y 18 to 72 and its lower lines are hidden behind panel 2. Panel 2 (front, lower-right) runs from about y 35 to 93 and is fully legible. Both panels are square-cornered rectangles with a thin light-blue (#5BC0EB) outline and no shadow. Two small dark-navy Kubernetes ship-wheel icons (#002060) act as bullet markers beside the two bullet points. Logos: KubeCon ship-wheel mark with KubeCon wordmark in purple-navy #2E2A5E; CloudNativeCon emblem (dark navy square with lighter blue-grey interlocking mark) with CloudNativeCon wordmark; 'Europe 2024' text beneath, flanked by two thin horizontal rules and separated from the CloudNativeCon logo by a thin vertical divider; Wiz outlined red wordmark at bottom right, with a cropped red arrow tip at the right slide edge.
Slide 19
kubeconfig - EKS
KubeCon
CloudNativeCon
Europe 2024
Do you know what you have in ~/.kube/config?
Don’t run untrusted kubeconfig’s (equivalent to local executions)
Required secret:
AWS creds
Role with eks: perms
WIZ
>>aws --region eu-west-1 eks get-token --cluster-name test
{
"kind": "ExecCredential",
"apiVersion": "client.authentication.k8s.io/v1beta1",
"spec": {},
"status": {
"expirationTimestamp": "2024-02-12T15:41:58Z",
"token": "k8s-aws-v1.aHR0…ViZA"
}
}
Visuals: Kubernetes helm-wheel bullet icons: four dark navy-black ship-wheel glyphs, three level-one bullets beside 'Do you know what you have in', 'Don’t run untrusted' and 'Required secret:', and two smaller level-two bullets beside 'AWS creds' and 'Role with eks: perms'. Key icon: a flat yellow (#FFC000) key with a round bow containing a white hole and a serrated bit at the lower right, pointing right, about 11% wide. Code box: a solid black (#000000) rectangle 45.9% wide and 42.2% high with a thin light-blue outline, containing white monospace text of a terminal output, shown unboxed by any image. KubeCon logo: dark purple (#326CE5-like, rendered #3D2F6B) Kubernetes wheel hexagon above the word 'KubeCon' in dark purple bold sans. CloudNativeCon logo: a dark indigo square with a white stylised 'N' mark next to the bold words 'CloudNativeCon'; a thin vertical divider separates the two logos, and 'Europe 2024' sits in small bold text beneath with horizontal rules on either side. Wiz logo: the wordmark 'WIZ' in a crimson (#E0234E) outline font with a four-point sparkle at the upper-right of the Z.
Slide 20
kubeconfig - GKE / Do you know what you / have in / ~/.kube/config? / Don’t run untrusted / kubeconfig’s / (equivalent to local / executions) / - name: gke_cluster / user: / exec: / apiVersion: / client.authentication.k8s.io/v1beta1 / command: gke-gcloud-auth-plugin.exe / installHint: Install gke-gcloud-auth-plugin / for use with kubectl by following / https://cloud.google.com/blog/products/containers- / kubernetes/kubectl-auth-changes-in-gke / provideClusterInfo: true / KubeCon / CloudNativeCon / Europe 2024 / wiz
Visuals: Two Kubernetes ship-wheel bullet icons in black, one beside each bulleted paragraph in the left column. One black rectangular code box (about 49.5% x, 17.9% y, 45.9% wide, 39.0% high) containing monospaced white text, a YAML kubeconfig excerpt for gke_cluster with exec authentication settings, with a thin light-blue border. Logos: the KubeCon wordmark with its ship-wheel mark (dark navy #2B2A6B), a vertical divider, the CloudNativeCon wordmark with a stylised icon (navy #2B2A6B), and the text Europe 2024 between two thin horizontal rules, all in the header band. The Wiz logo in the bottom-right is an outlined wordmark with a four-point sparkle, stroked in red-pink #D0104C on white.
Slide 21
kubeconfig - GKE
Do you know what you / have in / ~/.kube/config?
Don’t run untrusted / kubeconfig’s / (equivalent to local / executions)
Required secret:
GCP creds
Role with gke: perms
>gke-gcloud-auth-plugin.exe / { / "kind": "ExecCredential", / "apiVersion": / "client.authentication.k8s.io/v1beta1", / "spec": { / "interactive": false / }, / "status": { / "expirationTimestamp": "2024-02- / 12T08:20:14Z", / "token": "ya29…pQQiZC8g0177" / } / }
Visuals: Yellow key icon at lower left, beside the 'Required secret' bullets, flat yellow #FFC000 with a white circular hole at its bow and a notched bit at its tail. Black rectangular code panel at right (x 47.5%, y 42.1%, w 45.9%, h 45.3%) containing white monospace JSON-style text of an ExecCredential output. Kubernetes wheel bullet glyphs in dark navy #002060 before each bullet line and sub-bullet. KubeCon and CloudNativeCon Europe 2024 logos at top right in the title bar: KubeCon with a purple Kubernetes wheel mark above the word 'KubeCon', and CloudNativeCon with a dark indigo square mark above 'CloudNativeCon' and 'Europe 2024' beneath, separated by a thin vertical rule. Wiz outlined wordmark logo at bottom right in crimson #D0194B outline with a small four-point sparkle at top right.
Slide 22
kubeconfig - AKS
KubeCon / CloudNativeCon / Europe 2024
- name: clusterUser_shayb-resource-group_shayb- / threat-aks / user: / client-certificate-data: LS0tLS1CR...LS0tCg== / client-key-data: LS0tL...LS0K / token: fkoa...meh8n
Do you know what you / have in / ~/.kube/config?
Don’t run untrusted / kubeconfig’s / (equivalent to local / executions)
Required secret:
kubeconfig
Property / Value
Issuer / CN = ca
Subject / CN = masterclient,O = system:masters
Valid From / 25 Jan 2024, 1:28 p.m.
Valid To / 25 Jan 2026, 1:38 p.m.
Serial Number / F9:65:C1:33:5A:D3:70:B7:F1:AD:86:0C:9B:52:48:59 (331506111506955129473477289782317041753)
CA Cert / No
Key Size / 4096 bits
Fingerprint (SHA-1) / 5B:4E:72:6A:A2:75:1B:E2:1F:FF:53:83:98:1D:D4:B9:7B:32:D7:FB
Fingerprint (MD5) / 08:38:5B:B2:F1:30:7C:A8:13:8B:06:29:6E:FE:B4:B6
SANS
Wiz
Visuals: Four visual elements. (1) Black code box at top right, 45.9% wide and 20.2% tall, with thin light-blue border, showing a Kubernetes user entry in white monospace text: '- name: clusterUser_shayb-resource-group_shayb-threat-aks', 'user:', 'client-certificate-data: LS0tLS1CR...LS0tCg==', 'client-key-data: LS0tL...LS0K', 'token: fkoa...meh8n'. (2) Screenshot of a certificate details table in a light-blue bordered box at lower right, 50.3% wide and 41.3% tall, with a grey header row. Columns: Property and Value. Rows: Issuer = CN = ca; Subject = CN = masterclient,O = system:masters; Valid From = 25 Jan 2024, 1:28 p.m.; Valid To = 25 Jan 2026, 1:38 p.m.; Serial Number = F9:65:C1:33:5A:D3:70:B7:F1:AD:86:0C:9B:52:48:59 (331506111506955129473477289782317041753); CA Cert = No; Key Size = 4096 bits; Fingerprint (SHA-1) = 5B:4E:72:6A:A2:75:1B:E2:1F:FF:53:83:98:1D:D4:B9:7B:32:D7:FB; Fingerprint (MD5) = 08:38:5B:B2:F1:30:7C:A8:13:8B:06:29:6E:FE:B4:B6; SANS = blank. Text is small sans-serif, black on white. (3) Kubernetes helm-wheel bullet glyphs, black, drawn as small ship-wheel symbols, three large ones beside the bullet groups and one smaller one beside 'kubeconfig'. (4) Logos: KubeCon and CloudNativeCon Europe 2024 logo at top right in dark indigo, and Wiz wordmark logo with a sparkle in red outline at bottom right.
Slide 23
kubeconfig - Conclusions / KubeCon / CloudNativeCon / Europe 2024 / EKS / GKE / AKS / Leaky kubeconfig / != / Compromise / Leaky kubeconfig / != / Compromise / Leaky kubeconfig / == / long-term compromise* / * - under the default Local RBAC authentication mode
Visuals: One three-column by two-row table, drawn as filled rectangles with thin white gutters. Header row (y 42.6% to 48.4%, height 5.8%): three cells filled #59BBEA with bold dark navy Consolas text: EKS (column 1), GKE (column 2), AKS (column 3). Body row (y 48.4% to 63.1%, height 14.7%): three cells filled #D1E7F7 with navy #002060 Consolas regular text, each centred, three lines per cell. Column 1 (EKS): 'Leaky kubeconfig' / '!=' / 'Compromise'. Column 2 (GKE): 'Leaky kubeconfig' / '!=' / 'Compromise'. Column 3 (AKS): 'Leaky kubeconfig' / '==' / 'long-term compromise*'. No chart, photo or diagram. Icons and logos: a solid yellow (#FFC000-like) key icon bottom-left, consisting of a round bow with a hole and a toothed shaft; the KubeCon logo (purple hexagonal Kubernetes wheel mark with the word KubeCon in dark purple, a vertical divider, and a dark purple square CloudNativeCon mark with the words CloudNativeCon and Europe 2024 between two thin horizontal rules) top-right in the header band; the Wiz logo bottom-right as a red-outlined wordmark with a four-point sparkle above the Z.
Slide 24
kubeconfig – Other uses
Github search:
Client certificate
Tokenfile
Token
Username/password
Other exec’s
Visuals: Six code screenshots (editor/file views with line numbers, light grey text on white, thin light-blue borders) and two logos and two icons. Screenshot 1 (top right, boxed): YAML lines 'kind: Config', 'preferences: {}', 'users:', '- name: default', ' user:', ' client-certificate-data: LS0tLS1CRUdJTiBDRVJUSUZJQ0FURS0t' (truncated at right edge), ' client-key-data: LS0tLS1CRUdJTiBFQyBQUklWQVRFIEtFWS0tLS0t' (truncated). Screenshot 2 (below it, boxed): lines 16 'users:', 17 '- name: dfd', 18 ' user:', 19 ' tokenFile: /var/run/secrets/kubernetes.io/serviceaccount/token'. Screenshot 3 (centre, boxed, with a highlighted row): line 8 'users:', 9 '- name: "geddes"', 10 highlighted yellow-tinted row ' user:' with a small rounded '...' button at its left, 11 ' token: "kubec' (cut off by the next screenshot). Screenshot 4 (lower centre-right, boxed): line 42 '- name: gcp_k8s_predictions', 43 ' user:', 44 ' password: <gcp-predictions-cluster-password>', 45 ' username: admin'. Screenshot 5 (bottom, wide boxed): line 64 'user:', 65 ' exec:', 66 ' apiVersion: client.authentication.k8s.io/v1beta1', 67 ' args: ["ga-aws-dea-dev", "--exec", "aws --no-cli-auto-prompt --region ap-southeast-2 eks get-token', 68 ' --cluster-name infra-dev-eks"]', 69 ' command: assumego', 70 ' env:'. Logos: KubeCon and CloudNativeCon Europe 2024 logos in top right (KubeCon in dark navy wheel mark with navy text, CloudNativeCon in dark navy square mark with navy text, separated by a vertical divider and sub-line 'Europe 2024'). Wiz logo bottom right in red-outlined letters with a sparkle mark. Icons: small navy Kubernetes helm wheel icons before each bullet item (six total including the heading-less bullets: Client certificate, Tokenfile, Token, Username/password, Other exec’s). A yellow key icon bottom left, solid gold #F5B800 with a white circular bow.
Slide 25
kubeconfig / KubeCon / CloudNativeCon / Europe 2024 / Anomaly rules on kube- / audit / Secondary detections / Secrets scanning / Data exfiltration / solutions / Coding practices / Screenshot text: .docker / .kube / cache / config / gke_gcloud_auth_plugin_cache / 1 { / 2 "current_context": "gke_akhilesh123_us / 3 "access_token": "ya29.c.b0Aaekm1JIm3Zu / 4 "token_expiry": "2023-05-10T06:12:20Z" / 5 "extra_args": "" / 6 } / WIZ
Visuals: Red line icon of a siren or warning beacon (about 5.4% by 9.5% of slide) above the left column, flat red #EF4B4B with a base bar. Green icon of a paint bucket or jar with white drip shape and a handle loop (measured fill #59BF92) above the right column. Screenshot (696 by 172 px, boxed, not full-bleed) of a file explorer on the left, with a light grey vertical divider, showing folders .docker (collapsed) and .kube (expanded) containing cache (collapsed), config (file) and gke_gcloud_auth_plugin_cache (file, selected with a blue rounded outline). On the right is a code editor with line numbers 1 to 6 showing a JSON object with keys current_context, access_token, token_expiry and extra_args, and a horizontal scrollbar at the bottom; the image is outlined by a thin light-blue frame. A yellow key icon (bottom left) and the red-pink outlined WIZ wordmark with a small sparkle (bottom right) are logos. Logos in the header: KubeCon wheel mark in dark navy with the KubeCon wordmark, and a CloudNativeCon square mark in dark navy with the CloudNativeCon wordmark and the text Europe 2024 beneath, separated by a thin vertical divider.
Slide 26
Kubelet API Access
Kubelet has API???
From
https://github.com/kubernetes/kubernetes/blob/master/pkg/kubelet/server/server.go
s.addMetricsBucketMatcher("attach") / ws = new(restful.WebService) / ws. / Path("/attach") / ws.Route(ws.GET("/{podNamespace}/{podID}/{containerNam / e}"). / To(s.getAttach). / Operation("getAttach")) / ws.Route(ws.POST("/{podNamespace}/{podID}/{uid}/{containerName}"). / To(s.getAttach). / Operation("getAttach")) / ws.Route(ws.GET("/{podNamespace}/{podID}/{uid}/{contai / nerName}"). / To(s.getAttach). / Operation("getAttach")) / ws.Route(ws.POST("/{podNamespace}/{podID}/{uid}/{conta / inerName}"). / To(s.getAttach). / Operation("getAttach")) / s.restfulCont.Add(ws)
KubeCon CloudNativeCon Europe 2024
Wiz
Visuals: Three screenshots and one photo. (1) A terminal strip, full-width of the lower-middle area, with a black background and white monospace text: a process line beginning 'root 2410 1.3 1.7 1639620 126376 ? Ssl Jan25 281:48 /usr/local/bin/kubelet --enable-server --node-labels=agentpool=agentpool,kubernetes.azure.com/agentpool ...' followed by many kubelet flags such as --cgroup-driver=systemd, --address=0.0.0.0 (the word 'address' and value in red), --anonymous-auth=false, --authentication-token-webhook=true, --authorization-mode=Webhook, --kubeconfig=/var/lib/kubelet/kubeconfig, --max-pods=110, --read-only-port=0, --rotate-certificates=true, --tls-private-key-file=/etc/kubernetes/certs/kubeletserver.key; the strip is partially covered by the black code box and the photo. (2) A black code box with white Courier-style monospace text containing Go code of the restful WebService routes listed in the text element. (3) A photograph, boxed with a thin grey border and no rounding, showing a close-up of a dark metallic hood or dome-shaped fixture seen from below, with a glossy highlight on the dome at upper centre, a dark rectangular opening beneath it, desaturated grey-brown tones, soft diffuse light, and tight framing that crops the fixture at the edges. Icons: Kubernetes wheel icons in navy at both bullets. Logos: KubeCon wheel logo with CloudNativeCon logo at top right; Wiz wordmark outline at bottom right.
Slide 27
Kubelet API Access
kube-audit blind
Sensor events
Secondary activities only
Network exposure management
VPC flow logs
Secondary protection – Admission Controller / cloud policies
Visuals: Two icons and one photograph. Left icon: a red (#EF4444-like) flashing alarm/siren light with rays above it, on a base, outline style, centered above the left list at about x 20%, y 17%, w 6%, h 10%. Right icon: a green (#59BF92) filled cup or pot shape with a white drip and a handle, outlined in black, centered above the right list at about x 65.5%, y 17.4%, w 5.4%, h 10.4%. Photograph at bottom-left, boxed (not cropped to a circle, not full-bleed), rectangular, showing a close-up of a dark, grey-brown security-camera-like dome or round object mounted in a dark square recess in a light grey wall, lit from above with a soft highlight on the dome, dominant colours dark brown-black and grey; the image is a straight rectangle with thin dark edges. Logos: KubeCon logo (purple hexagonal ship's wheel mark over the word KubeCon in dark navy, top right); CloudNativeCon logo (dark navy-purple square mark over the words CloudNativeCon, with 'Europe 2024' below in navy, separated from KubeCon by a thin vertical divider); Wiz logo bottom-right in outline red-pink (#D6246E-like) with a small four-point sparkle at top right. Bullets are small black-navy ship-wheel (Kubernetes) glyphs in dark navy.
Slide 28
Management Interfaces / Kubernetes- / dashboard / Kubeflow / Airflow / dashboards / Addons dashboards / Lessons from the Cryptojacking Attack at Tesla / RedLock CSI Team / 02.20.18 6:00 AM
Visuals: A full-slide template image forms the cyan header band and the KubeCon and CloudNativeCon Europe 2024 logos. A screenshot of a browser window (macOS-style traffic-light dots, tab titled Pods - Kubernetes Dashboard, address bar localhost:8001/api/v1/namespaces/kube-system/services/https:kubernetes-dashboard:/proxy/#!/pod?namespace=kube-system) shows the Kubernetes dashboard Pods view with a blue top bar reading kubernetes and a Search field. The left sidebar lists Nodes, Persistent Volumes, Roles, Storage Classes, Namespace kube-system, Overview, Workloads, Cron Jobs, Daemon Sets, Deployments, Jobs, Pods (highlighted), Replica Sets, Replication Controllers, Stateful Sets, and Discovery and Load Balancing. Two line charts: CPU usage (y axis CPU (cores) 0 to 0.135 with ticks 0.030, 0.060, 0.090, 0.120; x axis Time 11:10 to 11:24; green filled area line near 0.12 throughout, no printed values besides axis ticks) and Memory usage (y axis Memory (bytes) 0 to 644 Mi with ticks 143 Mi, 286 Mi, 429 Mi, 572 Mi; x axis Time 11:10 to 11:24; blue filled line about 570 Mi flat with a small peak near 11:20). A Pods table with columns Name, Node, Status, Restarts, Age, CPU (cores), Memory (bytes) and rows: kubernetes-dashboard-7b9c7b, minikube, Running, 0, 27 minutes, 0, 19.746 Mi; heapster-qhq6r, minikube, Running, 0, 27 minutes, 0, 18.004 Mi; influxdb-grafana-77c7p, minikube, Running, 0, 27 minutes, 0, 43.926 Mi; kube-scheduler-minikube, minikube, Running, 0, 20 hours, 0.01, 11.930 Mi; etcd-minikube, minikube, Running, 0, 20 hours, 0.015, 58.445 Mi; one further partly visible row. A photograph of a man in a flat cap and dark jacket peering from a doorway at a burst of bright orange flame from a fire at upper left; the frame is cropped to a rectangle, warm lighting with orange and yellow highlights, red curtains and dark wood at right and a pale wall at left. A screenshot of an article card with a thin dark blue border showing the title Lessons from the Cryptojacking Attack at Tesla, the subtitle RedLock CSI Team and the date 02.20.18 6:00 AM on a light grey background. The Wiz logo, a red-outlined wordmark with a four-point sparkle, at bottom right. The KubeCon wheel logo and the CloudNativeCon square logo with a vertical divider line and Europe 2024 text at top right. Nine-spoke Kubernetes wheel icons in black serve as bullet markers.
Slide 29
Managmeent Interfaces
Anomaly rules on kube-
audit
Secondary activities
Network exposure
management
Secondary protection –
Admission Controller /
cloud policies
KubeCon
CloudNativeCon
Europe 2024
WIZ
Visuals: Two line icons above the columns. Left: a red (#F04E4E approx.) rotating siren/alarm light icon, centred around x 26%, y 22%, about 10% wide and 11% high, with red rays above and a red base bar. Right: a green (#59BF92) paint-bucket-style icon with a white dripping top and a dark outline, centred around x 69%, y 21%, about 5% wide and 10% high. Also the KubeCon + CloudNativeCon Europe 2024 logo lockup at top right: a dark purple (#2E2A5E approx.) Kubernetes wheel logo above 'KubeCon' text, a vertical divider, a dark purple square-pattern CloudNativeCon mark above 'CloudNativeCon' text, and 'Europe 2024' centred beneath with thin horizontal rules on each side. The Wiz logo at bottom right is a crimson (#D0104C approx.) outlined wordmark 'WIZ' with a four-point sparkle at its upper right. Bullets are small black ship-wheel (Kubernetes helm) glyphs, one per item.
Slide 30
kubectl proxy
Visuals: One photograph, boxed and centred in the white body area: a still of a young boy with short brown hair, wearing a dark red-brown jumper, looking to his left in a dim room. A bright white lamp or window glow is at upper right, a dark diagonal object (a beam or shadow) runs from upper centre down to the left, and a greenish patch is at lower right. The image is low resolution and slightly pixelated, with a black border at top and bottom, shown uncropped in a rectangle with no overlay or tint. Dominant colours are dark brown, black and warm orange-red. Also present: the KubeCon and CloudNativeCon Europe 2024 logo lockup at top right, consisting of a purple Kubernetes wheel mark with the word KubeCon, a vertical divider, a purple CloudNativeCon mark with the word CloudNativeCon, and the line 'Europe 2024' beneath with thin rules on either side; and the Wiz wordmark in outlined red-crimson letters with a four-point sparkle at top right, bottom right. A small grey dot sits at about x 11.8, y 50 on the left.
Slide 31
kubectl proxy / WTH is kubectl proxy? / kubectl proxy command does not go through the K8s API server / Could be any port depending on the –-port option / Jumper can be random and out of monitoring scope / KubeCon / CloudNativeCon / Europe 2024 / Attacker / Firewall / VM jumper / kubectl proxy --address="0.0.0.0" --port=8080 / Cluster / Control plane / API server / Data plane / Laptop / kubectl proxy --port=8080
Visuals: Hand-drawn architecture diagram in grey and black sketch lines on white. An grey silhouette figure labelled Attacker sits at the left, with a black arrow pointing right to an orange brick-wall Firewall icon with a black rounded outline and the label Firewall above it. A second black arrow points right from the firewall to a rounded white box labelled VM jumper, which has a pale pink rounded label beneath reading kubectl proxy --address="0.0.0.0" --port=8080. A long black line runs from the VM jumper box diagonally down-right to the API server. Below, a rounded white box labelled Laptop has a line running diagonally right to the API server, and beneath it a pale pink rounded label reads kubectl proxy --port=8080. On the right, a large rounded rectangle labelled Cluster with a blue Kubernetes helm logo at its top-left corner contains two rounded green-hatched panels: Control plane on the left containing a dashed rounded box labelled API server, and Data plane on the right. The two arrows from VM jumper and Laptop converge on the API server. A photograph sits at the upper right: a dark, low-light still of a young boy with short brown hair and a red-orange top, looking down and left, with a bright white light source at the right edge, warm and dark brown tones, shown as a rectangle with no border, not cropped to a circle, with no overlay.
Slide 32
Managmeent Interfaces
Anomaly rules on kube-audit (blind to proxy opening)
EDR/Sensor port open
Secondary activities
Network exposure management
Anti-fishing and anti-malware solutions for dev laptops
Secondary protection – AC / cloud policies
Visuals: Two flat line icons above the columns. Left: a red (#F05252) siren/alarm light with radiating rays, centred at about x 23.5%, y 22%, roughly 5.4% by 9.4% of the slide. Right: a green (#59BF92) filled paint-can or bucket with a black outline and a white paint drip and a curled cord-like handle, roughly 5.4% by 10.4% of the slide at x 66.1%, y 17.2%. Bullets in both lists are small black ship's-wheel (Kubernetes-style) glyphs, one per item, at about x 5.6% (left) and x 52% (right). Logos: KubeCon (purple hexagon with a helm wheel and the word KubeCon), CloudNativeCon (purple square-tile mark with the word CloudNativeCon), and 'Europe 2024' beneath, separated by a thin vertical divider and thin horizontal rules; the Wiz logo is a crimson outlined wordmark with a four-point sparkle at its top-right corner.
Slide 33
Control Plane / KubeCon / CloudNativeCon / Europe 2024 / Cloud credential leak / Cloud credential leak / K8s credential leak / EKS / GKE / AKS / Network exposure / Misconfig / Network exposure / Kubeconfig / kubectl proxy / Kubelet API access / Mgmt interfaces / K8s API access / Control plane
Visuals: Diagram of stacked rounded rectangles forming a control-plane stack, with no arrows or connectors. Row 1 (top, y 23.1%): three red #F04F50 boxes at x 35.0, 48.6 and 62.2, labelled Cloud / credential / leak, Cloud / credential / leak and K8s / credential / leak. Row 2 (y 36.8%): purple #4B3B71 boxes labelled EKS (x 35.0), GKE (x 48.6), AKS (x 62.2), and a red box labelled Network / exposure at x 76.1. Row 3 (y 50.5%): red box Misconfig at x 6.2, red box Network / exposure at x 20.6, purple box Kubeconfig spanning x 35.0 to 75.5 (width 40.5), and purple box kubectl / proxy at x 76.1. Row 4 (y 64.2%): purple box Kubelet / API access at x 6.2, purple box Mgmt / interfaces at x 20.6, purple box K8s API access spanning x 35.0 to 89.4 (width 54.4). Row 5 (bottom, y 77.9%): purple box Control plane spanning x 6.2 to 89.4 (width 83.2). Labels are white monospace text. Logos: KubeCon (dark navy hexagon ship wheel icon with KubeCon wordmark) and CloudNativeCon (navy square icon with CloudNativeCon wordmark and Europe 2024 line), separated by a thin vertical divider; Wiz logo (red outline wordmark with a four-point sparkle) at bottom right. No photographs. Boxes have a thin light grey outline and about 1% corner radius.
Slide 34
Use Case – GKE system:authenticated / misconfiguration
Visuals: One photograph, a still of a young boy with light brown hair and a cream knit sweater holding a dark rifle diagonally across his body. He looks down to his right. The background is an indoor room, blurred, with warm brown wooden furniture, a red object at upper left and white shelves. Warm, muted brown and beige tones. The image is a rectangular, uncropped-looking still with sharp square corners, no border, no shadow, placed as a box in the centre. It is low resolution with visible compression. One WIZ logo at bottom right: white letters outlined in magenta-pink with a small four-point sparkle at the top right.
Slide 35
system:authenticated misconfig / KubeCon / CloudNativeCon / Europe 2024 / system:authenticated sounds safe enough / Why won’t we bind admin perms to this group? / Any user with Google account -> system:authenticated
Visuals: Three small black ship's-wheel (Kubernetes helm) bullet glyphs, one beside each body line. Logos at top right: the KubeCon logo (a dark purple hexagonal helm icon with the word KubeCon beneath it) and, separated by a thin vertical divider, the CloudNativeCon logo (a dark purple square icon with a stylised N, with the words CloudNativeCon and Europe 2024 beneath it, with thin horizontal rules on either side of Europe 2024). Bottom-right corner: the Wiz logo drawn as red outlined letters WIZ with a small four-point sparkle at the top right of the Z. No photographs, charts, or tables.
Slides 36 to 62 continue in the full text file.
Download this deck
The hosted PDF of every library deck is free for readers of the SlideDeck Co newsletter. Join with your email and the viewer and download appear here.
Building a deck of your own? The SlideDeck Co Standard Deck is a slide library for business presentations: reviews, updates and plans.