The deck is a sales presentation from Complynet, a compliance provider for automotive dealers, branded for 700Credit and dated July 2022 on its title slide. It opens with Complynet's company history and then turns to the FTC Safeguards Rule, covering its original 2003 effective date, the October 2021 revision, the December 9, 2022 enforcement date for new provisions, and the penalty amount. The core of the deck walks through ten required compliance steps in order: establishing a safeguards team, written risk assessment, written information security program, information security training, phishing penetration testing, vendor assessments and agreements, access controls, technical requirements, written incident response plan, and written annual report to the board. Each step is shown with a repeated navigation graphic that tracks progress through the sequence, and most steps list the specific tasks involved. The closing section compares Complynet's offerings with those of other providers, listing which documents and services Complynet creates or performs versus those the dealer must build from templates, and ends with a contact slide for 700Credit.
Slides worth studying
Questions about this deck
How many slides does the Complynet Safeguards sales deck from 700Credit have?
The deck has 20 slides. Slide 1 is the title slide, which is branded for 700Credit and dated July 2022.
What penalty does the Complynet Safeguards deck give for violating the FTC Safeguards Rule?
Slide 3 states that penalties can be up to $46,517 per violation. The same slide lists the December 9, 2022 enforcement date for new provisions.
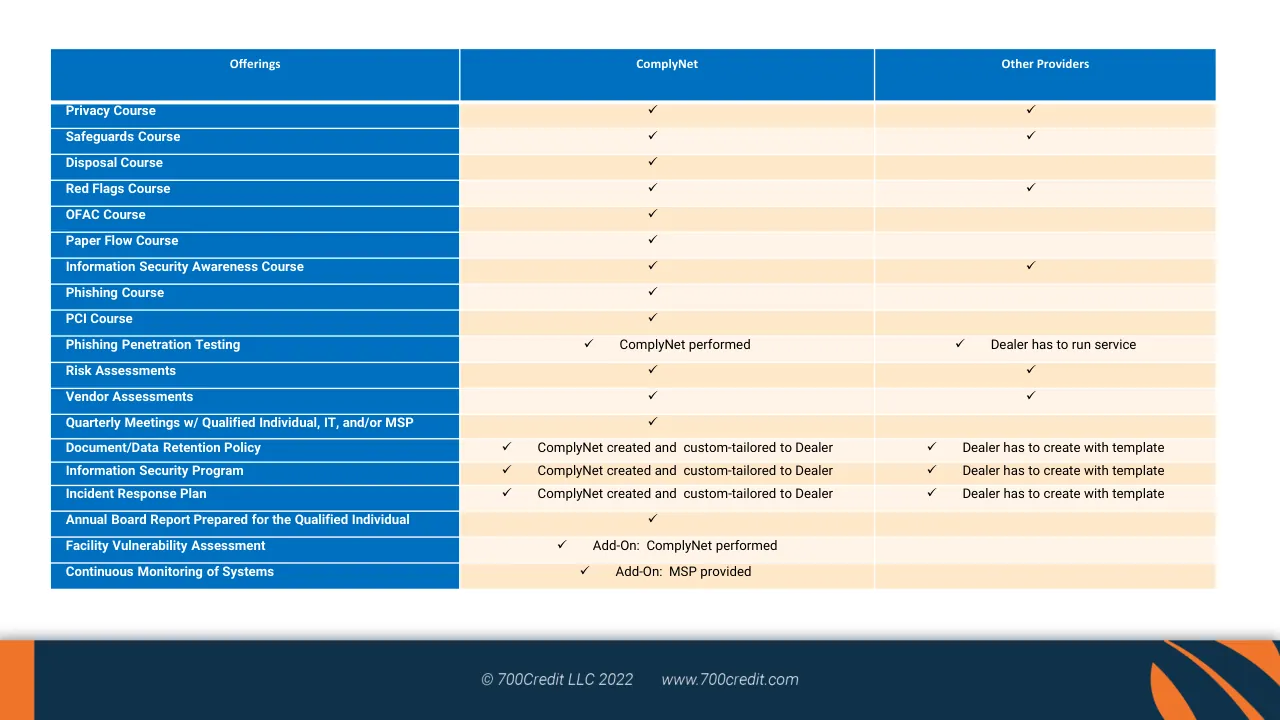
What does Complynet create for dealers compared with what dealers must build themselves, according to the Complynet offerings slide?
Slide 18 says ComplyNet creates and custom-tailors the Information Security Program, Incident Response Plan, and Document/Data Retention Policy to the dealer. For those items, other providers leave the dealer to create them with a template.
How is the Complynet Safeguards deck structured?
Slide 3 lists 10 steps to compliance, and slide 4 introduces them in order. Slides 4 through 16 then walk through each step, from establishing a safeguards team to the written annual report to the board.
Details
- Company: Complynet
- Year: 2022
- Type: Sales deck
- Industry: Automotive compliance
- Pages: 20
Review score: 6 out of 10, Needs substantial work
Presentation quality, judged with the SlideDeck Co review heuristic. Ask, evidence and idea merit are not rated here.
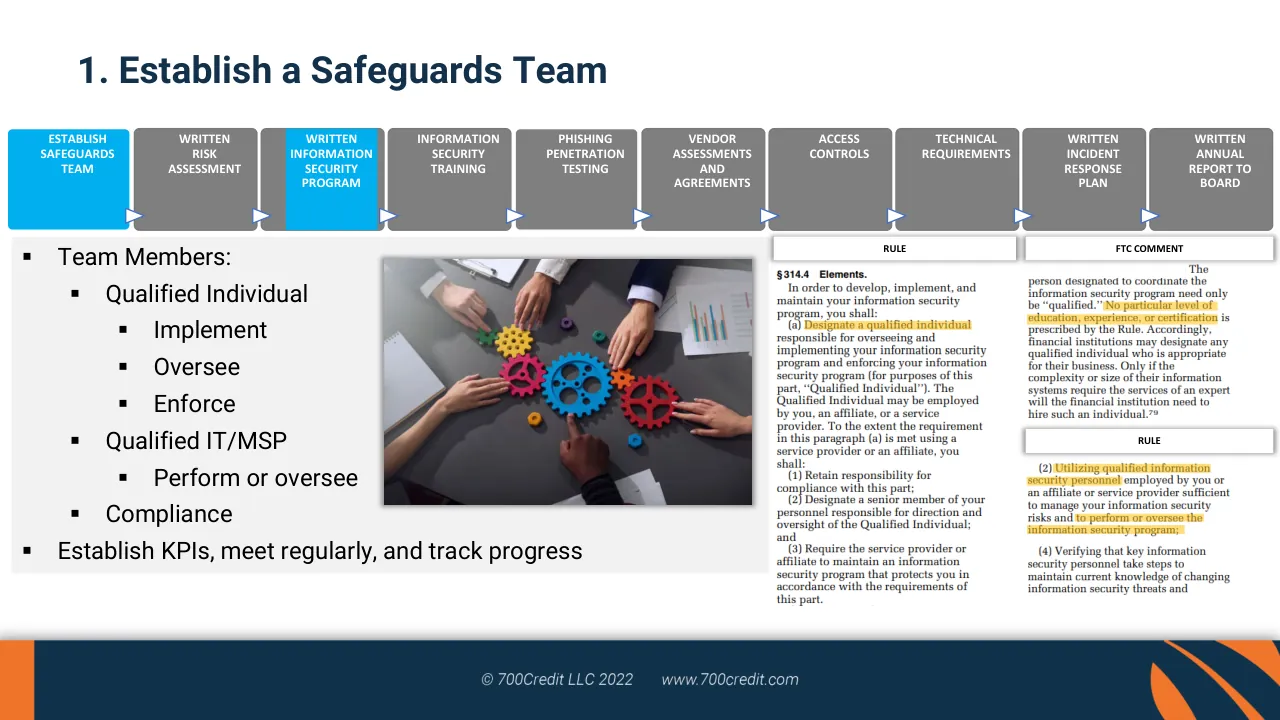
The deck has a clear route: history, rule facts, ten numbered steps with a progress tracker, a comparison table, pricing and contact. It is branded consistently and the facts table on slide 3 and the comparison on slide 18 are legible. But slide 4 highlights the wrong tracker step (step 3, 'Written Information Security Program', is lit on a 'Safeguards Team' slide) and the tracker repeats near-unchanged on most pages. The regulatory text excerpts on slides 4 to 16 are too small to read and compete with the bullets, and the stock images, tiny screenshots and duplicate slides (the two 'Technical Requirements' slides near-identical, and slide 6 repeating slide 5's layout) add clutter, so substantial revision is needed.
Worth keeping: Keep the ten-step numbered structure with the progress tracker, the facts table on slide 3, the checkmark comparison table on slide 18 and the consistent navy and orange branding.
Most useful repair: Fix the tracker highlight on slide 4, enlarge or cut the unreadable rule excerpts to a single pulled quote, and remove the duplicated Technical Requirements slides.
What would change the score: Replace the decorative stock photos and tiny screenshots with fewer, larger visuals that show what the dealer gets, and add a short summary slide connecting the steps to the comparison and pricing.
Confidence high. 20 of 20 pages inspected on contact sheets, 3 at readable size. Reviewed 2026-11-08. Model-assisted review (claude-sonnet-5-5).
Full text of the slides (20 slides)
Every slide's words and a description of its charts and images, so the deck can be searched and rebuilt. Also available as Markdown.
Slide 1
700Credit / CREDIT | COMPLIANCE | SOFT-PULLS / Complynet Safeguards Sales Deck / July 2022
Visuals: One full-bleed photograph of a car showroom. A smiling man in a light-grey shirt and a smiling woman in a light dress stand on the left. A man in a dark grey suit stands on the right and shakes hands with them at the front of a white SUV. Glass walls, steel beams and a ceiling light panel are visible behind them. Composition is a medium-wide shot with the subjects in the centre and the car's rear wheel at the lower right. Lighting is bright and even, from the showroom glazing. Dominant colours are slate navy and off-white. The photo is not cropped and is covered by a navy tint, about 55 percent opacity, that is probably a shape over the image. The logo is the 700Credit lockup: an orange circular swoosh mark, '700' in bold italic orange, 'Credit' in bold white sans-serif, and the tagline below in white capitals with orange vertical bar separators.
Slide 2
Complynet’s History
Founded in 1994
Automotive exclusive
End-to-end compliance
Tech-enabled solutions
Association endorsed
Over 3,000 rooftop partners
An End-to-End Compliance Solution Exclusively for Auto Dealers
Powered by
© 700Credit LLC 2022
www.700credit.com
Complynet
Home / Who We Are / Who We Serve / Solutions / Resources / Sign Up / Contact Us
Demo / Login / 800.653.1869
Environmental Health & Safety / EH&S Compliance Training, Task Management, Reporting
Human Resources / Employee Handbook, Policy Sign-Off, Benchmarking Training, Policy Management
Sales & Finance / Sales and F&I Compliance Training, Auditing, Reporting
Privacy and Safeguards / Safeguard Management Training, Policy, Vendor Management
GCA Guided Compliance Assistant / Guiding and enhancing our dealerships culture of compliance / Sign Up >
ABLE
Visuals: One photograph-style screenshot of a computer monitor (desktop display mockup) centred in a boxed frame at x 41.1%, y 22.4%, w 53.4%, h 53.2%, not cropped, not full-bleed, with a thin black bezel and a black tapered stand below it (black trapezoid, x 63.9%, y 71.9%, w 7.3%, h 11.0%, narrowing toward the base, drawn in #000000). The screen shows a website screenshot of complynet.com: a light grey browser address bar reading complynet.com at top, a white navigation bar with the COMPLYNET logo (black COMPLYNET with a blue N and E), menu items Home, Who We Are, Who We Serve, Solutions, Resources, Sign Up, Contact Us, and blue Demo and Login buttons with 800.653.1869. Below is a black hero area with a large faded headline (partly hidden, reading 'Assistant') and a centred white subtitle 'An End-to-End Compliance Solution Exclusively for Auto Dealers'. A large dark photograph of an open laptop lying on a dark surface with an orange-to-purple glowing keyboard and screen fills the lower screen, with warm orange and magenta light and dark shadows, shown in a wide, slightly low-angle view. A light grey-blue (#E3E8F0) popup panel overlays the top of the hero with four service tiles in two rows (Environmental Health & Safety, Human Resources, Sales & Finance, Privacy and Safeguards), each with a blue line icon, and a white GCA card at the right with a GCA logo, 'Guiding and enhancing our dealerships culture of compliance' and a light blue 'Sign Up >' button. At the right of the hero, a white GCA logo and 'Powered by' above a white ABLE logo. The footer band across the bottom is a full-width navy (#0F3049) vector band with an orange (#F47C20) vertical bar at the far left edge and orange and navy curved swoosh shapes at the far right. A white-to-transparent full-slide template graphic is placed behind everything.
Slide 3
Safeguards History
SAFEGUARDS RULE FACTS
Original Effective Date
2003
Revised
October 2021
Enforcement Date for New Provisions
December 9, 2022
Penalties
up to $46,517 per violation
ComplyNet InfoSec Solutions
8 years
Steps to Compliance
10
© 700Credit LLC 2022
www.700credit.com
Visuals: Table: header row merged across both columns, blue #0070C0 fill, containing a circular seal (about 5.5% of slide width) to the left of the white text SAFEGUARDS RULE FACTS. Six body rows with no column headers: row 1 Original Effective Date | 2003; row 2 Revised | October 2021; row 3 Enforcement Date for New Provisions | December 9, 2022; row 4 Penalties | up to $46,517 per violation; row 5 ComplyNet InfoSec Solutions | 8 years; row 6 Steps to Compliance | 10. Label cells are blue #0070C0 with white text; value cells alternate #FFE8CB (rows 1, 3, 5) and #FFF4E7 (rows 2, 4, 6) with black text; thin white gridlines separate rows and columns. Seal: a circular emblem with a green laurel ring, gold text around the rim reading FEDERAL TRADE COMMISSION, UNITED STATES OF AMERICA and MCMXV, a central light-blue shield with a gold scales of justice and an eagle below, dominant colours gold, green, blue and white, full circle not cropped, placed on the blue header. Footer logo: a white stylised swoosh/leaf shape cropped by the bottom-right corner of the slide. The full-slide background image is a white template with the footer band and swoosh; no photograph.
Slide 4
1. Establish a Safeguards Team / ESTABLISH SAFEGUARDS TEAM / WRITTEN RISK ASSESSMENT / WRITTEN INFORMATION SECURITY PROGRAM / INFORMATION SECURITY TRAINING / PHISHING PENETRATION TESTING / VENDOR ASSESSMENTS AND AGREEMENTS / ACCESS CONTROLS / TECHNICAL REQUIREMENTS / WRITTEN INCIDENT RESPONSE PLAN / WRITTEN ANNUAL REPORT TO BOARD / Team Members: / Qualified Individual / Implement / Oversee / Enforce / Qualified IT/MSP / Perform or oversee / Compliance / Establish KPIs, meet regularly, and track progress / RULE / FTC COMMENT / §314.4 Elements. / In order to develop, implement, and maintain your information security program, you shall: / (a) Designate a qualified individual responsible for overseeing and implementing your information security program and enforcing your information security program (for purposes of this part, 'Qualified Individual'). The Qualified Individual may be employed by you, an affiliate, or a service provider. To the extent the requirement in this paragraph (a) is met using a service provider or an affiliate, you shall: / (1) Retain responsibility for compliance with this part; / (2) Designate a senior member of your personnel responsible for direction and oversight of the Qualified Individual; and / (3) Require the service provider or affiliate to maintain an information security program that protects you in accordance with the requirements of this part. / The person designated to coordinate the information security program need only be 'qualified.' No particular level of education, experience, or certification is prescribed by the Rule. Accordingly, financial institutions may designate any qualified individual who is appropriate for their business. Only if the complexity or size of their information systems require the services of an expert will the financial institution need to hire such an individual.79 / RULE / (2) Utilizing qualified information security personnel employed by you or an affiliate or service provider sufficient to manage your information security risks and to perform or oversee the information security program; / (4) Verifying that key information security personnel take steps to maintain current knowledge of changing information security threats and / © 700Credit LLC 2022 / www.700credit.com
Visuals: Ten rectangular process tiles in a horizontal row, each with a white right-pointing outlined triangle arrow at its lower right edge. Tile 1 (ESTABLISH SAFEGUARDS TEAM) and tile 4 (WRITTEN INFORMATION SECURITY PROGRAM) are highlighted in bright blue #00B0F0; the other eight are grey #7F7F7F. Photograph: overhead view of about six people's hands touching multicoloured interlocking gears (blue centre gear, red, magenta, yellow, green, orange and small blue gears) on a dark grey table, with a notepad at left and a paper with a bar chart at upper right; full colour, not cropped, boxed with a thin white border and soft drop shadow. Right excerpt images are screenshots of regulation text: the left column shows the RULE text for section 314.4 with yellow highlights on 'Designate a qualified individual'; the upper right column shows FTC COMMENT text with yellow highlights on 'No particular level of education, experience, or certification'; the lower right column shows RULE text with yellow highlights on 'Utilizing qualified information security personnel' and 'to perform or oversee the information security program;'. Each excerpt is a boxed scan with black serif text on white. Header boxes above the excerpts are white with thin grey outlines. A navy footer band with an orange vertical bar at its left edge and an orange swoosh logo mark at its bottom right corner.
Slide 5
1. Establish a Safeguards Team
ESTABLISH SAFEGUARDS TEAM
WRITTEN RISK ASSESSMENT
WRITTEN INFORMATION SECURITY PROGRAM
INFORMATION SECURITY TRAINING
PHISHING PENETRATION TESTING
VENDOR ASSESSMENTS AND AGREEMENTS
ACCESS CONTROLS
TECHNICAL REQUIREMENTS
WRITTEN INCIDENT RESPONSE PLAN
WRITTEN ANNUAL REPORT TO BOARD
QUALIFIED INDIVIDUAL
Implement, Oversee, and Enforce
Map Customer Information (CI)
Answer Risk Assessment
Gather Current Plans/Policies
Safeguards
Team
Meet Quarterly
Track Progress
Resolve Issues
Annual Report
IT/MSP
Enable MFA/Encryption
Secure Networks/Close Ports
Anti-Virus and Firewall
Continuous Monitoring or Pen-Testing and Vulnerability Scans
COMPLYNET
Risk Assessments
Employee Trainings
Develop/Modify Plans/Policies
Vendor Management Tools
Guidance
RULE
§314.4 Elements.
In order to develop, implement, and maintain your information security program, you shall:
(a) Designate a qualified individual responsible for overseeing and implementing your information security program and enforcing your information security program (for purposes of this part, “Qualified Individual”). The Qualified Individual may be employed by you, an affiliate, or a service provider. To the extent the requirement in this paragraph (a) is met using a service provider or an affiliate, you shall:
(1) Retain responsibility for compliance with this part;
(2) Designate a senior member of your personnel responsible for direction and oversight of the Qualified Individual; and
(3) Require the service provider or affiliate to maintain an information security program that protects you in accordance with the requirements of this part.
FTC COMMENT
The person designated to coordinate the information security program need only be “qualified.” No particular level of education, experience, or certification is prescribed by the Rule. Accordingly, financial institutions may designate any qualified individual who is appropriate for their business. Only if the complexity or size of their information systems require the services of an expert will the financial institution need to hire such an individual.79
RULE
(2) Utilizing qualified information security personnel employed by you or an affiliate or service provider sufficient to manage your information security risks and to perform or oversee the information security program;
(4) Verifying that key information security personnel take steps to maintain current knowledge of changing information security threats and
© 700Credit LLC 2022
www.700credit.com
Visuals: 1) Process bar: ten rectangular tiles in a single row (about 0.6% to 99.4% across, y 17.9% to 32.0%), each with a small white right-pointing triangle outlined in blue at its bottom-left corner. Tiles 1 and 4 are blue #00B0F0; the others are grey #7F7F7F. Tile 4 overlaps the grey tile 3 behind it. 2) Grey panel #F2F2F2 with three blue #0070C0 boxes: QUALIFIED INDIVIDUAL at top centre with four square-bulleted lines; COMPLYNET at bottom-left with a COMPLYNET wordmark logo (grey COMPLY, blue NET) overlapping its top edge and five square-bulleted lines; IT/MSP at bottom-right with five square-bulleted lines. 3) Central navy triangle, apex at top, dark navy #001F5C fill with a soft blue glow and white outline, with a small blue #00B0F0 padlock icon near its apex and four square-bulleted lines in white bold Calibri. 4) Two screenshots of the regulation text (left: §314.4 rule text on white; right: FTC comment and rule excerpt on white), with yellow #FFFF00 highlighting on key phrases: “Designate a qualified individual”, “No particular level of education, experience, or certification”, “Utilizing qualified information security personnel”, “to perform or oversee the information security program;”. 5) White header boxes with thin grey shadow labelled RULE and FTC COMMENT. 6) Orange footer band with a white swoosh logo at bottom-right, cropped at the slide edge. Nothing is cropped in the diagram; no photographs are present.
Slide 6
2. Written Risk Assessment / ESTABLISH SAFEGUARDS TEAM / WRITTEN RISK ASSESSMENT / WRITTEN INFORMATION SECURITY PROGRAM / INFORMATION SECURITY TRAINING / PHISHING PENETRATION TESTING / VENDOR ASSESSMENTS AND AGREEMENTS / ACCESS CONTROLS / TECHNICAL REQUIREMENTS / WRITTEN INCIDENT RESPONSE PLAN / WRITTEN ANNUAL REPORT TO BOARD / Map (where CI is stored, who accesses, and how) / Identify risks / Evaluate and categorize risks / Examine controls/safeguards / Mitigate risks (or accept and address) / Periodically reexamine controls/safeguards / RULE / (2) Identify and manage the data, personnel, devices, systems, and facilities that enable you to achieve business purposes in accordance with their relative importance to business objectives and your risk strategy; / RULE / (b) Base your information security program on a risk assessment that identifies reasonably foreseeable internal and external risks to the security, confidentiality, and integrity of customer information that could result in the unauthorized disclosure, misuse, alteration, destruction, or other compromise of such information, and assesses the sufficiency of any safeguards in place to control these risks. (1) The risk assessment shall be written and shall include: (i) Criteria for the evaluation and categorization of identified security risks or threats you face; (ii) Criteria for the assessment of the confidentiality, integrity, and availability of your information systems and customer information, including the adequacy of the existing controls in the context of the identified risks or threats you face; and / ABLE / Logout / My Assigned / Resources / Manage Users / Manage Company / Admin / My Account / HI, Adam Crowell / Use the buttons below for a quick access to your training, policies, and others. / My Training / My Policies / My Assessments / My eTask / My Forms / My Complaints / My Assessments / Do you ever see customer information left unattended on sales desks or in the service area? / Do you have posters at your facility that promote safeguarding information? / Are employees required to change their password on all computers, systems, and applications within 90 days? / Do you conduct regular checkups to see how effective your cybersecurity is? / Has anyone within your organization had a password stolen (to your knowledge)? / Do you regularly scan your network and get a report on potential weaknesses to address? / Do you have a company wide spam filter in place? / Are all firewalls and anti-virus software up to date? / Do you have a data/document retention policy? / Chat / © 700Credit LLC 2022 / www.700credit.com
Visuals: Ten rectangular process boxes with white bold uppercase labels, three in bright blue and seven in grey, each with a small white right-pointing triangle with blue outline at its bottom-left edge as a flow marker. Right of the bullet panel are two white RULE header boxes, two scanned black-on-white serif text excerpts of regulatory rule text (the (2) excerpt and the (b) excerpt), and a monitor showing the ABLE web application: a black bezel, a dark header bar with the ABLE logo, a navigation row, a red-and-white banner reading HI, Adam Crowell with five tab buttons, a light grey My Assessments panel with a three-column grid of small white question cards with radio buttons, and a blue Chat button at lower right; a black trapezoid stand sits under the monitor. The footer band has an orange vertical bar at its left edge and an orange swoosh graphic at its right edge.
Slide 7
3. Written Information Security Program
ESTABLISH SAFEGUARDS TEAM
WRITTEN RISK ASSESSMENT
WRITTEN INFORMATION SECURITY PROGRAM
INFORMATION SECURITY TRAINING
PHISHING PENETRATION TESTING
VENDOR ASSESSMENTS AND AGREEMENTS
ACCESS CONTROLS
TECHNICAL REQUIREMENTS
WRITTEN INCIDENT RESPONSE PLAN
WRITTEN ANNUAL REPORT TO BOARD
Created based upon the risk assessment
Includes:
Administrative safeguards
Technical safeguards
Physical safeguards
Establishes clear roles and responsibilities
Automotive specific and custom-tailored
Clear and concise
Periodically evaluated and adjusted
RULE
§314.3 Standards for safeguarding customer information.
(a) Information security program. You shall develop, implement, and maintain a comprehensive information security program that is written in one or more readily accessible parts and contains administrative, technical, and physical safeguards that are appropriate to your size and complexity, the nature and scope of your activities, and the sensitivity of any customer information at issue. The information security program shall include the elements set forth in § 314.4 and shall be reasonably designed to achieve the objectives of this part, as set forth in paragraph (b) of this section.
RULE
(g) Evaluate and adjust your information security program in light of the results of the testing and monitoring required by paragraph (d) of this section; any material changes to your operations or business arrangements; the results of risk assessments performed under paragraph (b)(2) of this section; or any other circumstances that you know or have reason to know may have a material impact on your information security program.
© 700Credit LLC 2022
www.700credit.com
Visuals: Ten rectangular process boxes in a single row with small white triangle arrows on their bottom-right corners. Boxes 1 to 3 are bright blue and boxes 4 to 10 are mid grey. A photograph of a blue circuit board with a central cluster of metal gears, lit evenly with a bright white glow at the centre, shown in a sharp-cornered box with a thin drop shadow, full colour and not cropped. Two rectangular screenshots of printed regulation text (serif, black on white) under white RULE header boxes. A grey panel holding a bulleted list. Orange footer band with a white curved swoosh logo at the bottom right corner.
Slide 8
4. Information Security Training / ESTABLISH SAFEGUARDS TEAM / WRITTEN RISK ASSESSMENT / WRITTEN INFORMATION SECURITY PROGRAM / INFORMATION SECURITY TRAINING / PHISHING PENETRATION TESTING / VENDOR ASSESSMENTS AND AGREEMENTS / ACCESS CONTROLS / TECHNICAL REQUIREMENTS / WRITTEN INCIDENT RESPONSE PLAN / WRITTEN ANNUAL REPORT TO BOARD / RULE / RULE / Mandatory Training / (Job-Role and Industry-Specific): / Privacy / Privacy for the Shop / Safeguards / Safeguards for the Shop / Disposal / Information Security Awareness / Phishing / PCI / (1) Providing your personnel with security awareness training that is updated as necessary to reflect risks identified by the risk assessment; / (4) Verifying that key information security personnel take steps to maintain current knowledge of changing information security threats and countermeasures. / COMPLYNET / Privacy for Shop / Privacy for Shop / © 700Credit LLC 2022 / www.700credit.com
Visuals: Ten rectangular process boxes in a single horizontal row, each with a small white right-pointing triangle with blue outline at its bottom right corner. The first four boxes (ESTABLISH SAFEGUARDS TEAM, WRITTEN RISK ASSESSMENT, WRITTEN INFORMATION SECURITY PROGRAM, INFORMATION SECURITY TRAINING) are bright blue #00B0F0; the remaining six (PHISHING PENETRATION TESTING, VENDOR ASSESSMENTS AND AGREEMENTS, ACCESS CONTROLS, TECHNICAL REQUIREMENTS, WRITTEN INCIDENT RESPONSE PLAN, WRITTEN ANNUAL REPORT TO BOARD) are mid grey #7F7F7F. Each box is about 9.6 percent wide and 14.1 percent tall. Illustration: a black-bezelled desktop monitor on a black trapezoid stand, showing a white course screen with the COMPLYNET logo (COMPLY in navy, NET in blue), blue title text Privacy for Shop, two small blue pill buttons, and a blue bottom bar with small white text Privacy for Shop and a white arrow at right. Two white RULE header boxes with thin grey outline and bold black RULE label sit above two serif text columns quoting rule (1) and rule (4). The centre panel is a light grey #F2F2F2 rectangle with a bulleted list. Not cropped; no photographs; no chart or table.
Slide 9
5. Phishing Penetration Testing
ESTABLISH SAFEGUARDS TEAM
WRITTEN RISK ASSESSMENT
WRITTEN INFORMATION SECURITY PROGRAM
INFORMATION SECURITY TRAINING
PHISHING PENETRATION TESTING
VENDOR ASSESSMENTS AND AGREEMENTS
ACCESS CONTROLS
TECHNICAL REQUIREMENTS
WRITTEN INCIDENT RESPONSE PLAN
WRITTEN ANNUAL REPORT TO BOARD
FTC COMMENT
. Penetration testing, as defined by the Final Rule, is a process through which testers “attempt to circumvent or defeat the security features of an information system.” 56 One way such security features are tested is through social engineering and phishing.57 The fact that the testing involves employees with access to the information system, rather than just the system itself, does not exclude such tests from the definition of “penetration testing.” Attempted social engineering and phishing are important parts of testing the security of information systems and would not be excluded by this definition.
FTC COMMENT FOOTNOTE
57 Indeed, Workshop participant Scott Wallace noted, in conducting penetration testing, “the first thing [he does]” is generally to “prepare for the phishing campaign.” Remarks of Scott Wallace, Safeguards Workshop Tr., supra note 17, at 131–32.
91% of all hacking starts with phishing
Greatest known risk
ComplyNet conducts phishing pen-testing
© 700Credit LLC 2022 www.700credit.com
Visuals: Ten process boxes in one row: five blue (#00B0F0) and five grey (#7F7F7F), each with a small white right-pointing triangle with blue outline at its lower right edge, overlapping the next box. A scanned legal document excerpt in the left column (serif body text, black on white, with a yellow highlight over 'Attempted social engineering and phishing are important parts of testing the security of information systems'). A grey panel (#F2F2F2) containing three bullets, and below them a flat-screen monitor illustration with black bezel and black stand showing a dashboard screenshot: six coloured tiles across the top (green 66 DELIVERED, purple 8 OPENED, yellow 2 CLICKED, red 0 DATA EXTENDED, light blue 2 RECEIVED TRAINING, blue 0 REPORTED PHISHING), each with a one-line caption beneath; below these two pie charts: left pie mostly blue (about 97%) with a small red slice (about 3%), legend 'Included Tests Average Passed vs Failed Average Messages Sent: 22', 'Passed: 21.33 (97.0%)', 'Failed: 0.67 (3.0%)'; right pie mostly green (about 92%) with small purple, dark and yellow slices, titled 'Most Severe Action by User for all Tests', legend includes 'Email Opened: 6 (6.5%)' and 'Clicked Link in Email: 2 (2.0%)' with other small legend text largely illegible at this size. Footer contains no imagery besides the swoosh logo.
Slide 10
6. Vendor Assessments and Agreements
ESTABLISH SAFEGUARDS TEAM
WRITTEN RISK ASSESSMENT
WRITTEN INFORMATION SECURITY PROGRAM
INFORMATION SECURITY TRAINING
PHISHING PENETRATION TESTING
VENDOR ASSESSMENTS AND AGREEMENTS
ACCESS CONTROLS
TECHNICAL REQUIREMENTS
WRITTEN INCIDENT RESPONSE PLAN
WRITTEN ANNUAL REPORT TO BOARD
RULE
(f) Oversee service providers, by:
(1) Taking reasonable steps to select and retain service providers that are capable of maintaining appropriate safeguards for the customer information at issue;
(2) Requiring your service providers by contract to implement and maintain such safeguards; and
(3) Periodically assessing your service providers based on the risk they present and the continued adequacy of their safeguards.
COMMENT FOOTNOTE
If it is infeasible for the service provider to meet these requirements then the financial institution's Qualified Individual must work with the service provider to develop compensating controls or cease doing business with the service provider.
Vendor Management
Vendor Assessments (1:many)
Vendor Agreements (1:many)
© 700Credit LLC 2022
www.700credit.com
Visuals: Three desktop-monitor mockups with black bezels and black stands, showing screenshots of the ABLE web application. Monitor 1 (top-left of the cluster, about x 23.3-48.7%, y 42.6-65.6%) shows the Vendor Management page: a centred heading 'Vendor Management', a Change Company dropdown, tabs My Vendors and Add Vendors, a search field 'Search Attached Vendors' with a green Search button, and a table with columns Name, Agreement Exists, Signed Date, Assessment Assigned, Assessment Completed, Address, Score; rows: Test Vendor 5 (6/26/2022, 6/26/2022, 6/27/2022, 123 any st, any town, Ohio 12345, 94), vendor 4 (6/12/2022, 6/15/2022, 6/16/2022, 123 vendor rd, vendor city, Florida 12345, 25), test vendor (6/7/2022, 123 any st, any city, Florida 12345, N/A), vendor test2 (6/8/2022, 123 any st, any city, Ohio 12345, N/A), AutomotoHR (6/21/2022, 30110 Boat Haven Drive, Canyon Lake, California 92587, N/A). A blue Help button sits bottom-right. Monitor 2 (about x 49.1-73.9%, y 51.9-74.9%) overlaps the grey panel and shows the Vendor Assessment page with tabs Info, Assessment, Agreement, Resend Request, a red delete icon and close icon, and a table with columns Question, Answer, Pass; rows include 'Has your company experienced a data breach or security event in the past year?' Yes with red X; 'When an employee is terminated at your company, are assigned devices collected and is access to email and information security systems immediately disabled?' No with red X; 'Does your company maintain appropriate safeguards to protect any customer information entrusted to your company?' Yes with green check; 'Has your company designated person(s) to implement, oversee, and enforce your company's information security program?' Yes with green check; 'Are all systems that warehouse customer information (at rest and in transit) encrypted with multi-factor authentication enabled?' Yes with green check; 'Does your company have a cybersecurity policy that covers data breach of customer information that is entrusted to your company?' Yes with green check; 'Are your company's firewalls and anti-virus software up-to-date and patched?' Yes with green check; 'Does your company provide information security personnel with security updates and training sufficient to address relevant security risks?' Yes with green check. Monitor 3 (about x 74.5-99.4%, y 60.7-83.6%) overlaps the lower-right of the grey panel and shows the Vendor Agreement page: heading 'Vendor Agreement', a blue Download link, and a dense block of underlined and small body text titled INTENDED THIRD-PARTY BENEFICIARY AGREEMENT FOR SAFEGUARDING CUSTOMER INFORMATION with numbered sections I. Definitions, II. Intended Third-Party Beneficiaries, III. Agreement to Implement and Maintain Safeguards. The rule and footnote texts are shown as plain serif black text on white with the two label boxes. Process tiles carry small white triangular arrowheads at their lower-right corners pointing right.
Slide 11
7. Access Controls
ESTABLISH SAFEGUARDS TEAM
WRITTEN RISK ASSESSMENT
WRITTEN INFORMATION SECURITY PROGRAM
INFORMATION SECURITY TRAINING
PHISHING PENETRATION TESTING
VENDOR ASSESSMENTS AND AGREEMENTS
ACCESS CONTROLS
TECHNICAL REQUIREMENTS
WRITTEN INCIDENT RESPONSE PLAN
WRITTEN ANNUAL REPORT TO BOARD
RULE
(c) Design and implement safeguards / to control the risks you identify through / risk assessment, including by: / (1) Implementing and periodically / reviewing access controls, including / technical and, as appropriate, physical / controls to: / (i) Authenticate and permit access / only to authorized users to protect / against the unauthorized acquisition of / customer information; and / (ii) Limit authorized users' access / only to customer information that they / need to perform their duties and / functions, or, in the case of customers, / to access their own information; / (2) Identify and manage the data, / personnel, devices, systems, and / facilities that enable you to achieve / business purposes in accordance with / their relative importance to business / objectives and your risk strategy;
RULE
(6)(i) Develop, implement, and / maintain procedures for the secure / disposal of customer information in any / format no later than two years after the / last date the information is used in / connection with the provision of a / product or service to the customer to / which it relates, unless such / information is necessary for business / operations or for other legitimate / business purposes, is otherwise required / to be retained by law or regulation, or / where targeted disposal is not / reasonably feasible due to the manner in / which the information is maintained; / and / (ii) Periodically review your data / retention policy to minimize the / unnecessary retention of data; / (7) Adopt procedures for change / management; and / (8) Implement policies, procedures, / and controls designed to monitor and / log the activity of authorized users and / detect unauthorized access or use of, or / tampering with, customer information / by such users.
Grant limited access
Monitor and log activity
Detect unauthorized use, access or / tampering
Adopt change management procedures
Onboarding and offboarding
Systems administrators?
Data and document retention and disposal
© 700Credit LLC 2022 www.700credit.com
Visuals: Ten process boxes in a row, drawn as rounded-corner rectangles with white text: seven are bright blue (#00B0F0) and three are grey (#7F7F7F), left to right: ESTABLISH SAFEGUARDS TEAM, WRITTEN RISK ASSESSMENT, WRITTEN INFORMATION SECURITY PROGRAM, INFORMATION SECURITY TRAINING, PHISHING PENETRATION TESTING, VENDOR ASSESSMENTS AND AGREEMENTS, ACCESS CONTROLS (blue), TECHNICAL REQUIREMENTS, WRITTEN INCIDENT RESPONSE PLAN, WRITTEN ANNUAL REPORT TO BOARD (grey). Nine small white right-pointing triangles with blue outlines sit at the lower-right corner of boxes 1 to 9 to show flow. Below the boxes are two small white RULE header boxes with grey drop shadows, then two scanned text blocks in a serif (Times-like) black font on white, reproducing regulatory rule text. A photograph sits centred at x 40.1% to 58.3%, y 46.7% to 68.3%: a close view of a hand holding a white key card to a card reader with a keypad mounted on a glass and metal door frame; a blue-tinted digital overlay shows two padlock icons and a faint fingerprint-like graphic; it is rectangular, unbordered and not cropped to a shape; dominant colours are steel blue, grey and white, lit with cool even light. The right panel is a flat light grey box holding black square-bullet text. The footer has a dark charcoal vertical strip at the far left (x 0 to 2.6%) and a white swoosh graphic in the bottom-right corner, which is a decorative brand mark rather than a legible logo.
Slide 12
8. Technical Requirements / ESTABLISH SAFEGUARDS TEAM / WRITTEN RISK ASSESSMENT / WRITTEN INFORMATION SECURITY PROGRAM / INFORMATION SECURITY TRAINING / PHISHING PENETRATION TESTING / VENDOR ASSESSMENTS AND AGREEMENTS / ACCESS CONTROLS / TECHNICAL REQUIREMENTS / WRITTEN INCIDENT RESPONSE PLAN / WRITTEN ANNUAL REPORT TO BOARD / RULE / RULE / (3) Protect by encryption all customer information held or transmitted by you both in transit over external networks and at rest. To the extent you determine that encryption of customer information, either in transit over external networks or at rest, is infeasible, you may instead secure such customer information using effective alternative compensating controls reviewed and approved by your Qualified Individual; / (4) Adopt secure development practices for in-house developed applications utilized by you for transmitting, accessing, or storing customer information and procedures for evaluating, assessing, or testing the security of externally developed applications you utilize to transmit, access, or store customer information; / (5) Implement multi-factor authentication for any individual accessing any information system, unless your Qualified Individual has approved in writing the use of reasonably equivalent or more secure access controls; / (d)(1) Regularly test or otherwise monitor the effectiveness of the safeguards' key controls, systems, and procedures, including those to detect actual and attempted attacks on, or intrusions into, information systems. / (2) For information systems, the monitoring and testing shall include continuous monitoring or periodic penetration testing and vulnerability assessments. Absent effective continuous monitoring or other systems to detect, on an ongoing basis, changes in information systems that may create vulnerabilities, you shall conduct: / (i) Annual penetration testing of your information systems determined each given year based on relevant identified risks in accordance with the risk assessment; and / (ii) Vulnerability assessments, including any systemic scans or reviews of information systems reasonably designed to identify publicly known security vulnerabilities in your information systems based on the risk assessment, at least every six months; and whenever there are material changes to your operations or business arrangements; and whenever there are circumstances you know or have reason to know may have a material impact on your information security program. / Encryption / Multi-factor authentication (MFA) / Continuous monitoring / Absent effective continuous monitoring, at least annual penetration testing and vulnerability scans every six months / © 700Credit LLC 2022 / www.700credit.com
Visuals: Three photographs stacked in the centre column at x 47.1 to 63.0 percent, each boxed with a thin white border and slight drop shadow. Top: a close-up of an ornate blue-silver key lying diagonally over a blue-tinted binary digital background, lit from above, cool blue dominant. Middle: a top-down view of two hands tapping a tablet on a wooden table; the tablet screen shows a padlock icon above a login form with User Name and Password fields and a blue LOGIN button, and a smartphone to the right shows a padlock icon; warm brown wood and blue screen tones. Bottom: a security camera in the foreground against a blue digital city-network graphic with lock, wifi and cloud icons and a red-orange glow at the right edge. Small thumbnails of the same three images sit beside the bullets: a key thumbnail beside Encryption, a tablet thumbnail beside Multi-factor authentication (MFA), and a camera thumbnail below the last bullet. The two text columns on the left are photographed printed regulation text, with yellow highlighter marks on Absent effective continuous monitoring, you shall conduct:, Annual penetration testing, Vulnerability assessments, and at least every six months.
Slide 13
8. Technical Requirements / ESTABLISH SAFEGUARDS TEAM / WRITTEN RISK ASSESSMENT / WRITTEN INFORMATION SECURITY PROGRAM / INFORMATION SECURITY TRAINING / PHISHING PENETRATION TESTING / VENDOR ASSESSMENTS AND AGREEMENTS / ACCESS CONTROLS / TECHNICAL REQUIREMENTS / WRITTEN INCIDENT RESPONSE PLAN / WRITTEN ANNUAL REPORT TO BOARD / RULE / (m) Penetration testing means a test methodology in which assessors attempt to circumvent or defeat the security features of an information system by attempting penetration of databases or controls from outside or inside your information systems. / FTC COMMENT / Commission does not agree. Penetration testing, as defined by the Final Rule, is a process through which testers “attempt to circumvent or defeat the security features of an information system.” 56 One way such security / Vulnerability scan – looks for weaknesses (inexpensive – free tools are available) / Penetration testing – can I get inside? How far can I get? What can I do? (requires “ethical hacker” and is very expensive) / Artificial intelligence (“AI”) programs do not meet the FTC’s qualifications for “assessors” in previous enforcement actions / “Assessors” have been defined as independent third-party professionals with experience and cybersecurity certifications / TIP: IF you are offered inexpensive “next gen” penetration testing with AI, it is likely just a vulnerability scan / Continuous monitoring – 24/7/365 security that detects and stops intruders (once reserved for large companies – is now affordable to all) / Encryption / Multi-factor authentication (MFA) / Continuous monitoring / Absent effective continuous monitoring, at least annual penetration testing and vulnerability scans every six months / © 700Credit LLC 2022 www.700credit.com
Visuals: Ten process boxes in a row: eight blue (#00B0F0) boxes labelled ESTABLISH SAFEGUARDS TEAM, WRITTEN RISK ASSESSMENT, WRITTEN INFORMATION SECURITY PROGRAM, INFORMATION SECURITY TRAINING, PHISHING PENETRATION TESTING, VENDOR ASSESSMENTS AND AGREEMENTS, ACCESS CONTROLS, TECHNICAL REQUIREMENTS, followed by two grey (#7F7F7F) boxes WRITTEN INCIDENT RESPONSE PLAN and WRITTEN ANNUAL REPORT TO BOARD; each box has a small white triangular arrow tip at its lower-right edge pointing right to the next box. Photograph of a white neoclassical government building with a central portico, a US flag on a pole at left, green lawn and paved steps in the foreground, a clear blue sky, daylight, full colour, boxed with no border and not cropped. Below it, a white label box marked RULE with a small image of printed legal text (serif type) showing the words Penetration testing and assessors highlighted in yellow. Below that, a white label box marked FTC COMMENT and a second printed-text image of serif text with the word testers highlighted in yellow. Three small square-bullet icons are not present; the right-panel images are small thumbnails: a blue-toned image of a key (Encryption), a photo of hands holding a tablet showing a padlock with a phone beside it (Multi-factor authentication), and a blue digital-tech image of a camera or sensor over circuit graphics (Continuous monitoring). The white swoosh logo at bottom right is a corner logo of 700Credit.
Slide 14
8. Technical Requirements
ESTABLISH SAFEGUARDS TEAM
WRITTEN RISK ASSESSMENT
WRITTEN INFORMATION SECURITY PROGRAM
INFORMATION SECURITY TRAINING
PHISHING PENETRATION TESTING
VENDOR ASSESSMENTS AND AGREEMENTS
ACCESS CONTROLS
TECHNICAL REQUIREMENTS
WRITTEN INCIDENT RESPONSE PLAN
WRITTEN ANNUAL REPORT TO BOARD
Recommendations:
Establish continuous threat monitoring
IT/MSPs have tools that they prefer to use
Encryption
Multi-factor authentication (MFA)
Continuous monitoring
Absent effective continuous monitoring, at least annual penetration testing and vulnerability scans every six months
© 700Credit LLC 2022
www.700credit.com
Visuals: Photograph: a male security operator in a white shirt with a headset microphone sits at a white desk, seen in side three-quarter profile facing left. In front of him is a wall of four flat-panel monitors in a 2x2 arrangement, each showing a grid of CCTV camera feeds of empty rooms, hallways and staircases in cool blue tones. He is typing on a black keyboard, with a black mouse to the right. Composition: landscape, boxed (not full-bleed, not cropped), with a soft grey drop shadow around the rectangle. Lighting: cool, even indoor light with blue cast. Dominant colours: blue, grey, white, black. Three small square-ish icons sit beside the right panel text: (1) a blue key on a textured blue fabric background, next to Encryption; (2) a laptop screen showing a padlock and login field with two hands typing, a phone at the right edge, on a reddish-brown background, next to Multi-factor authentication; (3) a camera silhouette over a digital circuit-board pattern on a blue-to-red gradient, below the sub-bullet text. Each icon has a soft shadow copy offset slightly behind it. Process diagram: ten rounded rectangles (blue #00B0F0 for steps 1 to 8, grey #7F7F7F for steps 9 and 10) with nine small white right-pointing triangles with blue outline at the lower-right of each of steps 1 to 9, forming a left-to-right flow. Right panel: light grey rectangle #F2F2F2 with no visible border.
Slide 15
9. Written Incident Response Plan / ESTABLISH SAFEGUARDS TEAM / WRITTEN RISK ASSESSMENT / WRITTEN INFORMATION SECURITY PROGRAM / INFORMATION SECURITY TRAINING / PHISHING PENETRATION TESTING / VENDOR ASSESSMENTS AND AGREEMENTS / ACCESS CONTROLS / TECHNICAL REQUIREMENTS / WRITTEN INCIDENT RESPONSE PLAN / WRITTEN ANNUAL REPORT TO BOARD / RULE / (h) Establish a written incident response plan designed to promptly respond to, and recover from, any security event materially affecting the confidentiality, integrity, or availability of customer information in your control. Such incident response plan shall address the following areas: / RULE / (1) The goals of the incident response plan; / (2) The internal processes for responding to a security event; / (3) The definition of clear roles, responsibilities, and levels of decision-making authority; / (4) External and internal communications and information sharing; / (5) Identification of requirements for the remediation of any identified weaknesses in information systems and associated controls; / (6) Documentation and reporting regarding security events and related incident response activities; and / (7) The evaluation and revision as necessary of the incident response plan following a security event. / Incident Response: / Respond / Recover / Remediate / Revise / © 700Credit LLC 2022 / www.700credit.com
Visuals: One photograph: a square crop of a man in a dark suit, seen from behind-left, index finger extended toward a glowing touch interface. Large glowing silver-blue letters reading RESPONSE span the upper half, with a red-outlined open padlock in orange and red in the centre-left. Hexagonal grid icons (cloud with arrow, magnifier, padlock, gear) fill the left edge. Lighting is dark and cool with blue highlights; dominant colours are navy, royal blue and orange-red. The photo is boxed, not full-bleed, with a soft drop shadow. Two text-based images of legal rule text (white background, black serif type) sit in the left and middle columns under RULE headers. No charts, tables or logos besides the swoosh mark in the footer corner.
Slide 16
10. Written Annual Report to Board
ESTABLISH SAFEGUARDS TEAM
WRITTEN RISK ASSESSMENT
WRITTEN INFORMATION SECURITY PROGRAM
INFORMATION SECURITY TRAINING
PHISHING PENETRATION TESTING
VENDOR ASSESSMENTS AND AGREEMENTS
ACCESS CONTROLS
TECHNICAL REQUIREMENTS
WRITTEN INCIDENT RESPONSE PLAN
WRITTEN ANNUAL REPORT TO BOARD
RULE
(i) Require your Qualified Individual to report in writing, regularly and at least annually, to your board of directors or equivalent governing body. If no such board of directors or equivalent governing body exists, such report shall be timely presented to a senior officer responsible for your information security program. The report shall include the following information:
(1) The overall status of the information security program and your compliance with this part; and
(2) Material matters related to the information security program, addressing issues such as risk assessment, risk management and control decisions, service provider arrangements, results of testing, security events or violations and management's responses thereto, and recommendations for changes in the information security program.
Overall status – compliance
Risks assessed
Risks managed and controlled
Service provider arrangements
Testing results
Security violations, events, and responses
Proposed changes
© 700Credit LLC 2022 www.700credit.com
Visuals: Ten process boxes in a horizontal row, each a rounded blue rectangle with a small white triangular arrowhead on its right edge pointing to the next box: 1 ESTABLISH SAFEGUARDS TEAM; 2 WRITTEN RISK ASSESSMENT; 3 WRITTEN INFORMATION SECURITY PROGRAM; 4 INFORMATION SECURITY TRAINING; 5 PHISHING PENETRATION TESTING; 6 VENDOR ASSESSMENTS AND AGREEMENTS; 7 ACCESS CONTROLS; 8 TECHNICAL REQUIREMENTS; 9 WRITTEN INCIDENT RESPONSE PLAN; 10 WRITTEN ANNUAL REPORT TO BOARD. Photograph in the middle column: a hand holds a white stylus pointing at a tablet on a black folding stand; the tablet screen shows a pie chart in blue and orange and several bar charts; in the foreground a white ceramic cup and a pen lie on a light wooden desk; the blurred office background shows dark furniture and orange chairs. Shallow depth of field, natural daylight from the left, warm neutral tones with blue and orange accents; the photo is a full rectangle, not cropped, with a soft grey drop shadow. Left column: a raster image of printed regulation text in a serif face on white. Right: bullet list on a light grey panel.
Slide 17
FEATURES SUMMARY
Assigned Compliance Success Consultant
Compliance Management System
Information Security Awareness Training:
Privacy
Privacy for the Shop
Safeguards
Safeguards for the Shop
Disposal
Information Security Awareness
Phishing
PCI
Phishing Penetration Testing
Written Risk Assessments
Onsite Facility Vulnerability Assessments
Vendor Assessments and Agreements
Quarterly Meetings with Qualified Individual/IT/MSP
Written Data/Document Retention Policy
Written Information Security Program
Written Data and Technology Use Policy
Written Incident Response Plan
Annual Written Report to the Board
GUIDED
COMPLIANCE
ASSISTANT
PRIVACY – SAFEGUARDS
© 700Credit LLC 2022
www.700credit.com
Visuals: Logo: GCA (Guided Compliance Assistant) mark, bold dark navy letters G, C and A with a light blue circular emblem inside the C, beside stacked text GUIDED / COMPLIANCE / ASSISTANT / PRIVACY – SAFEGUARDS. Three desktop monitors with silver stands and grey bases, cast soft grey shadows, staggered diagonally. Monitor 1 (upper left) shows a white screen with COMPLYNET wordmark, blue Privacy heading, small grey paragraph and two small blue buttons. Monitor 2 (middle) shows a dashboard with a row of six coloured tiles (green, purple, yellow, red, teal, blue) above two blue and green dots and a multicolour area chart with green, orange and blue filled curves over a time axis, with a small legend. Monitor 3 (lower right) shows an ABLE-branded white screen titled Assessments Assigned with a grid of small white cards and one blue button at lower right. Blue features panel (solid blue #0070C0) with white list text; square bullets, sub-items indented. Footer: orange band with a thin dark charcoal bar at its left edge and a white curved swoosh graphic at the right end.
Slide 18
Offerings
ComplyNet
Other Providers
Privacy Course
✓
✓
Safeguards Course
✓
✓
Disposal Course
✓
Red Flags Course
✓
✓
OFAC Course
✓
Paper Flow Course
✓
Information Security Awareness Course
✓
✓
Phishing Course
✓
PCI Course
✓
Phishing Penetration Testing
✓ ComplyNet performed
✓ Dealer has to run service
Risk Assessments
✓
✓
Vendor Assessments
✓
✓
Quarterly Meetings w/ Qualified Individual, IT, and/or MSP
✓
Document/Data Retention Policy
✓ ComplyNet created and custom-tailored to Dealer
✓ Dealer has to create with template
Information Security Program
✓ ComplyNet created and custom-tailored to Dealer
✓ Dealer has to create with template
Incident Response Plan
✓ ComplyNet created and custom-tailored to Dealer
✓ Dealer has to create with template
Annual Board Report Prepared for the Qualified Individual
✓
Facility Vulnerability Assessment
✓ Add-On: ComplyNet performed
Continuous Monitoring of Systems
✓ Add-On: MSP provided
© 700Credit LLC 2022 www.700credit.com
Visuals: Table: columns are Offerings, ComplyNet and Other Providers. Rows, with ComplyNet value then Other Providers value: Privacy Course (✓, ✓); Safeguards Course (✓, ✓); Disposal Course (✓, blank); Red Flags Course (✓, ✓); OFAC Course (✓, blank); Paper Flow Course (✓, blank); Information Security Awareness Course (✓, ✓); Phishing Course (✓, blank); PCI Course (✓, blank); Phishing Penetration Testing (✓ ComplyNet performed, ✓ Dealer has to run service); Risk Assessments (✓, ✓); Vendor Assessments (✓, ✓); Quarterly Meetings w/ Qualified Individual, IT, and/or MSP (✓, blank); Document/Data Retention Policy (✓ ComplyNet created and custom-tailored to Dealer, ✓ Dealer has to create with template); Information Security Program (✓ ComplyNet created and custom-tailored to Dealer, ✓ Dealer has to create with template); Incident Response Plan (✓ ComplyNet created and custom-tailored to Dealer, ✓ Dealer has to create with template); Annual Board Report Prepared for the Qualified Individual (✓, blank); Facility Vulnerability Assessment (✓ Add-On: ComplyNet performed, blank); Continuous Monitoring of Systems (✓ Add-On: MSP provided, blank). No chart, photograph or logo in the table. Decorative footer swoosh: two curved orange stripes over a navy shape at the bottom-right corner, cropped by the slide edge.
Slide 19
Pricing
As your partner, we make pricing transparent:
Service
Suggested Monthly Rooftop Pricing
GCA Environmental - Health - Safety
$299
GCA Sales - Finance - Advertising
$299
GCA Privacy - Safeguards
$299
GCA Deluxe (2 GCA Programs)
$549
GCA Premier (3 GCA Programs)
$799
Onsite Assessments
+ $100 per annual visit
Visuals: Full-bleed photograph of an automotive service bay or showroom: a car's rear quarter panel and alloy wheel are visible at the right edge, with two people's legs and dress shoes standing on a glossy dark floor at the bottom centre, overhead ceiling structures and light fixtures at the top, and a white car at the far right. The photo is covered by a dark navy tint overlay that mutes it to blue-grey tones. The white card is a rectangular boxed panel with square corners and no shadow, containing a two-column table with 7 rows including the header row: header row has columns 'Service' and 'Suggested Monthly Rooftop Pricing'; rows are: 'GCA Environmental - Health - Safety' with '$299'; 'GCA Sales - Finance - Advertising' with '$299'; 'GCA Privacy - Safeguards' with '$299'; 'GCA Deluxe (2 GCA Programs)' with '$549'; 'GCA Premier (3 GCA Programs)' with '$799'; 'Onsite Assessments' with '+ $100 per annual visit'. The Service column is blue; the price column alternates peach and cream. The logo is an orange stylised leaf or swoosh mark made of two curved petal shapes with a diagonal stroke, at the bottom right.
Slide 20
700Credit
CREDIT | COMPLIANCE | SOFT-PULLS
Contact 700Credit Today for Help
[email protected] | (866) 273-3848
Visuals: One photograph covering the whole slide, with a navy tint over it. Subject: a car dealership showroom in which a man in a grey shirt and a woman with curly hair in a light dress stand on the left, smiling, while a man in a dark grey suit on the right hands over a car key fob. A white or silver SUV is parked at the right edge, and tall glass walls, steel beams, and ceiling lights are visible above. Composition is a wide landscape frame; the people are centred left to centre, and the car runs off the right edge. Lighting is soft daylight through the glass. Dominant colours are slate and navy blue, with white car bodywork and grey clothing. The photo is not boxed and is full-bleed. A navy tint of about 70% opacity sits over the photo. The 700Credit logo is placed over the photo and overlaps the couple and the car door.
Download this deck
The hosted PDF of every library deck is free for readers of the SlideDeck Co newsletter. Join with your email and the viewer and download appear here.
Writing a sales deck of your own? The SlideDeck Co Sales Deck is a slide library with a priced services proposal and a Word statement of work.